Author: Optrics

  • Beyond Basic Monitoring: How to Prevent Database Disasters Before Users Notice

    Beyond Basic Monitoring: How to Prevent Database Disasters Before Users Notice

    Avoiding the Common Pitfalls in Database Performance Monitoring

    In today’s data-driven business environment, database performance can make or break your organization’s operations. When databases slow down or crash, everything from customer experiences to internal operations can grind to a halt. Yet many IT teams continue to fall into common monitoring traps that leave them vulnerable to unexpected downtime and performance issues.

    Why Database Monitoring Matters Now More Than Ever

    As databases become increasingly complex and mission-critical, the stakes for proper monitoring have never been higher. Consider these common scenarios that might sound familiar:

    • Your team receives complaints about application slowdowns, but your basic monitoring shows “all systems normal”
    • You’re flooded with alerts, but can’t distinguish between critical issues and minor anomalies
    • Your database seems fine from the backend, but users are experiencing significant delays

    These scenarios represent more than just technical challenges—they translate directly to business impact. According to industry research, unplanned downtime can cost organizations thousands of dollars per minute, not to mention the long-term damage to customer trust and team morale.

    Overcoming Database Monitoring Challenges with ManageEngine

    ManageEngine’s Site24x7 offers comprehensive solutions to these common monitoring pitfalls. Instead of basic status monitoring, it provides deep visibility into:

    • Transaction-level performance metrics: Track query execution times, identify bottlenecks, and optimize database operations before users notice slowdowns
    • Intelligent alerting: Configure meaningful alerts based on baseline performance metrics, reducing alert fatigue while ensuring critical issues get immediate attention
    • End-user experience monitoring: Understand how database performance affects actual application performance from the user perspective

    The platform’s real-time monitoring capabilities help IT teams shift from reactive firefighting to proactive performance management. By establishing baseline metrics and tracking deviations, you can identify potential issues before they impact business operations.

    Best Practices for Effective Database Monitoring

    To maximize the benefits of tools like ManageEngine Site24x7, consider implementing these best practices:

    1. Set meaningful baselines: Understand what “normal” looks like for your database performance during different operational periods
    2. Configure targeted alerts: Create alerts based on thresholds that reflect actual business impact, not just technical metrics
    3. Monitor from multiple perspectives: Look beyond server-side metrics to include client-side performance and user experience
    4. Regularly review system logs: Proactively analyze trends to spot potential issues before they trigger alerts
    5. Implement automated remediation: Use ManageEngine’s automation capabilities to address common issues without manual intervention

    Take Control of Your Database Performance Today

    As database environments continue to grow in complexity, particularly with hybrid and cloud deployments, having a comprehensive monitoring strategy becomes ever more critical. ManageEngine Network Configuration Manager provides the tools you need to avoid the common pitfalls that lead to performance issues and downtime.

    🔍 Could your current database monitoring approach be leaving blind spots that put your business at risk? Schedule a demo of ManageEngine Site24x7 today and discover how comprehensive performance monitoring can transform your database management strategy.


    Contact Us Today

  • The Invisible Network Threat: Why 60% of Companies Are Unknowingly Creating Security Blind Spots

    The Invisible Network Threat: Why 60% of Companies Are Unknowingly Creating Security Blind Spots

    Bridging the Gap: Integrating Configuration and Asset Management for Network Success

    In today’s complex IT environments, the distinction between configuration management and asset management often gets blurred. Yet, understanding and effectively implementing both are crucial for maintaining secure, efficient enterprise networks. While configuration management focuses on maintaining the setup and operational status of network devices, asset management tracks IT assets throughout their lifecycle—from procurement to disposal. When integrated properly, these two disciplines create a powerful foundation for network management.

    I remember consulting with a mid-sized financial company that was experiencing frequent network outages. Their IT team was diligent about tracking assets, but configuration changes were happening without proper documentation. The disconnect between these two systems created blind spots that led to security vulnerabilities and performance issues. Once they implemented an integrated approach, network incidents decreased by nearly 60% within just three months.

    The Growing Complexity of Enterprise Networks 🌐

    Managing today’s enterprise networks presents significant challenges:

    • Expanding attack surfaces require meticulous configuration control
    • Remote and hybrid work environments have dispersed assets across numerous locations
    • Regulatory compliance demands comprehensive visibility into both configurations and assets
    • Cloud and on-premises hybrid infrastructures create complex management scenarios

    According to recent industry studies, organizations with integrated configuration and asset management experience 45% fewer security incidents and reduce network downtime by up to 30%. These numbers highlight the tangible benefits of breaking down management silos.

    Are Your Network Management Practices Creating Blind Spots?

    Consider this: When was the last time your organization conducted a comprehensive audit comparing your asset inventory against your network configurations? If you’re like most organizations, the answer might reveal concerning gaps in your network visibility.

    Benefits of Integration: Beyond the Basics 🔒

    Enhanced Security Posture

    Integrating configuration and asset management creates a comprehensive security foundation by:

    • Identifying unauthorized devices that may appear in configurations but not in asset records
    • Ensuring proper security controls are consistently applied across all assets
    • Facilitating faster incident response through immediate access to accurate device information
    • Supporting vulnerability management by linking assets to their current configurations

    Operational Efficiency

    The operational benefits extend beyond security:

    1. Reduced troubleshooting time when network issues arise
    2. Streamlined compliance reporting with comprehensive data sources
    3. Improved budget planning with better visibility into asset lifecycles
    4. Enhanced change management with clear configuration baselines

    Building Your Integrated Approach

    The path to integration doesn’t have to be overwhelming. Start by:

    1. Conducting an assessment of your current configuration and asset management processes
    2. Identifying critical gaps where information isn’t flowing between systems
    3. Implementing automated tools that can synchronize data between configuration and asset repositories
    4. Establishing governance procedures that ensure ongoing integration

    Real-World Implementation Success

    A global manufacturing company recently unified their previously separate configuration and asset management systems through API integrations and automated workflows. The result? Their mean time to detect network anomalies dropped from days to hours, and they identified over 200 previously unknown devices connecting to their network.

    The Road Ahead

    As networks continue to grow in complexity, the integration of configuration and asset management will move from being a best practice to an essential requirement. Organizations that embrace this integrated approach now will build stronger foundations for future innovations like AI-driven network management and predictive maintenance.

    🚨 Don’t wait for a security incident or network failure to highlight gaps in your management approach. Take action today to assess how well your configuration and asset management practices align, and begin building bridges between these crucial disciplines.

    Are you ready to transform your network management approach? The competitive advantage of a well-managed network begins with integration.


    Contact Us Today

  • KnowBe4: Unraveling the Leader in Cybersecurity Training

    KnowBe4: Unraveling the Leader in Cybersecurity Training

    KnowBe4: Unraveling the Leader in Cybersecurity Training

    KnowBe4 has emerged as a pivotal force in the realm of cybersecurity, offering a comprehensive suite of training modules designed to equip organizations with the knowledge to fend off cyber threats. Through a blend of engaging training material and automated phishing simulations, KnowBe4 arms employees with the necessary skills to identify and mitigate potential cyber attacks, fostering a culture of security awareness training across various sectors.

    At the core of KnowBe4’s success lies its commitment to innovation within the cybersecurity training landscape. By continuously updating its training modules to reflect the latest cyber threats and trends, KnowBe4 ensures that organizations are always one step ahead. This proactive approach to cybersecurity education is complemented by KnowBe4’s use of real-world phishing simulations, allowing employees to experience the dynamics of actual phishing attempts in a controlled environment.

    Unlocking the Essence of KnowBe4

    KnowBe4 Security Awareness Training

    KnowBe4 stands out in the cybersecurity space through its unique amalgamation of automated phishing simulations, comprehensive training materials, and an extensive library of training modules. This blend not only demystifies the complex world of cyber threats but also empowers organizations to build a resilient and informed workforce. KnowBe4’s platform is designed to cater to various learning styles, ensuring that every employee can effectively contribute to their organization’s cyber defense strategy.

    How KnowBe4 Empowers Organizations Through Cybersecurity Training

    KnowBe4 empowers organizations by providing a robust framework of training modules that cover a wide range of cyber threats, including real-world phishing scenarios. Its managed service approach ensures that businesses can implement a tailored security training program that aligns with their specific needs and threats. By leveraging KnowBe4’s comprehensive training tools, organizations can significantly enhance their employees’ ability to recognize and respond to cyber threats, effectively reducing the risk of a successful attack.

    The Unique Approach of KnowBe4 to Security Awareness

    KnowBe4s Security 
 Awareness Training Cycle

    KnowBe4’s unique approach to security training revolves around creating a culture of continuous learning and vigilance. Unlike traditional security training programs, KnowBe4 engages users with interactive content and real-life simulations that mirror the latest phishing tactics. This method ensures that employees are not only well-versed in theoretical knowledge but are also prepared to apply this knowledge in practical, real-world situations, making it a leader in fostering security awareness.

    Analyzing KnowBe4’s Offerings

    KnowBe4’s offerings are a testament to its leadership in the cybersecurity training industry. Its platform provides a comprehensive suite of tools and resources that cater to the evolving needs of modern organizations seeking to bolster their cyber defenses.

    Human Risk Management

    Human risk is growing exponentially as technology becomes more woven into everyday routines. Recent research from KnowBe4 indicates 62% of surveyed organizations experienced one or more cyber incidents in the past year linked to human risk.  Their new HRM+ platform focuses on combatting this specific area.  On average, these businesses encountered three different types of breaches three times each, with 96% involving employees who clicked malicious links or opened harmful attachments.

    The Pros of Implementing KnowBe4 in Your Security Strategy

    Integrating KnowBe4 into an organization’s security strategy introduces a proactive layer of defense against cyber threats.

    KnowBe4’s training solutions offer several advantages, including increased awareness of phishing scams, a reduction in successful cyber attacks, and the cultivation of a security-first culture within organizations. By leveraging KnowBe4’s automated phishing simulations and engaging training modules, companies can significantly enhance their workforce’s ability to identify and neutralize potential threats, thereby strengthening their overall security posture.

    The Verdict from the Market

    KnowBe4’s market standing is a reflection of its effectiveness in enhancing organizational security through comprehensive training programs.

    How Businesses Are Leveraging KnowBe4 for Enhanced Security

    Organizations across industries are leveraging KnowBe4’s training solutions to fortify their defenses against cyber threats. The platform’s user-friendly approach and up-to-date content have made it a preferred choice for businesses seeking to elevate their security awareness levels.

    Customer Insights: Real Feedback from KnowBe4 Users

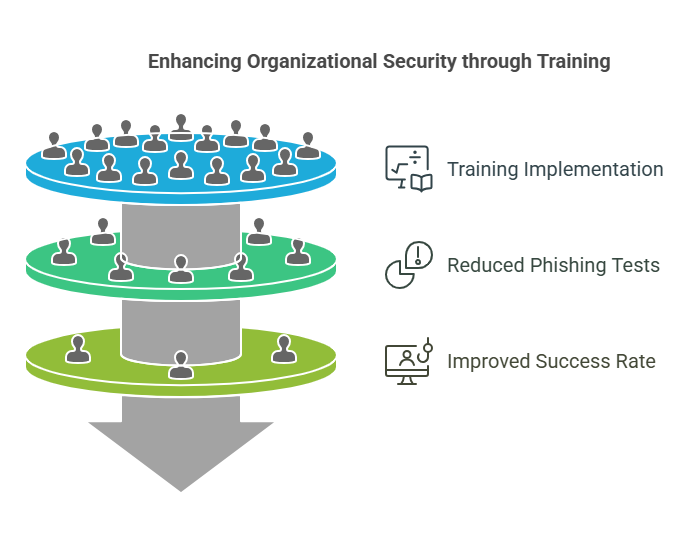
    Enhancing Organizational Security Through Training

    Feedback from KnowBe4 users highlights the platform’s impact in reducing the frequency and success rate of phishing tests, underscoring the tangible benefits of its training programs in improving organizational security.

    Why KnowBe4 Stands Out Amidst a Sea of Options

    KnowBe4 sets itself apart in the crowded field of cybersecurity training by understanding that the human element is both the biggest asset and the weakest link in cyber defense. Its platform combines security awareness with interactive training, making it easier for organizations to foster a culture of vigilance against phishing attempts and other cyber threats. KnowBe4’s platform continually updates its fresh content, ensuring users are prepared for the latest security challenges. This approach not only educates but empowers employees across organizations worldwide to make smarter security decisions, solidifying KnowBe4’s position as a leader in the awareness training platform space.

    Book Your KnowBe4 Demo Now

  • Top 5 Wifi Security Tweaks and How They Protect Your Network

    Top 5 Wifi Security Tweaks and How They Protect Your Network

    Top 5 Wifi Security Tweaks and How They Protect Your Network

    Enhancing wifi security is crucial for protecting your network from unauthorized access and cyber threats. By implementing simple security tweaks, you can significantly reduce the risk of your network being compromised. These measures include updating the router’s firmware, using unique passwords, and adjusting your encryption settings, all of which safeguard your network against potential breaches.
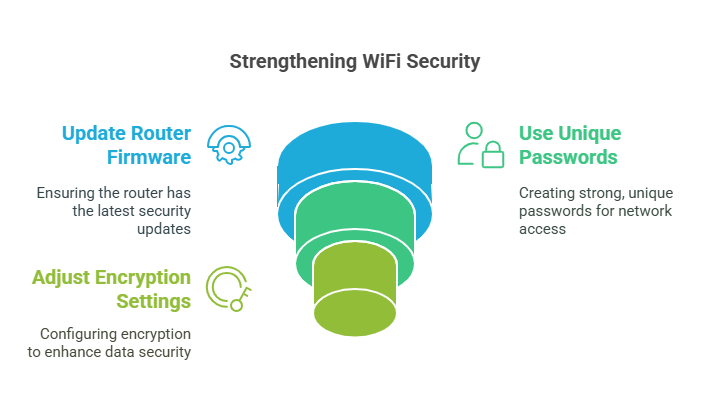
    Top 5 Wifi Security Tweaks

    One effective security tweak is to ensure your router’s firmware is regularly updated. Firmware updates often contain security enhancements and bug fixes that protect your network. Additionally, using a unique password for your wifi network prevents unauthorized access, making it difficult for hackers to gain entry. Encryption settings also play a vital role; by choosing advanced encryption methods, you ensure that the data transmitted over your network is secure.

    Moreover, disabling features that compromise security, such as remote access, and creating separate networks for guests, further enhances network protection. These wifi security tweaks are essential for maintaining a secure internet connection, protecting personal information, and preventing unauthorized access to your network. By staying informed and applying these simple yet effective measures, you can enjoy a safer online experience.

    Understanding the Importance of Wi-Fi Security

    Wi-Fi security is fundamental in today’s digitally connected world. It acts as the first line of defense against cyber threats that can compromise personal data and sensitive information. Ensuring your Wi-Fi network is secure prevents unauthorized access and protects against potential cyber-attacks, safeguarding your online activities.

    Without proper security measures, your network becomes an easy target for hackers. This vulnerability can lead to the theft of personal information, financial loss, and even identity theft. Therefore, understanding and implementing Wi-Fi security measures is crucial for anyone who uses the internet.

    The Risks of an Unprotected Wi-Fi Network
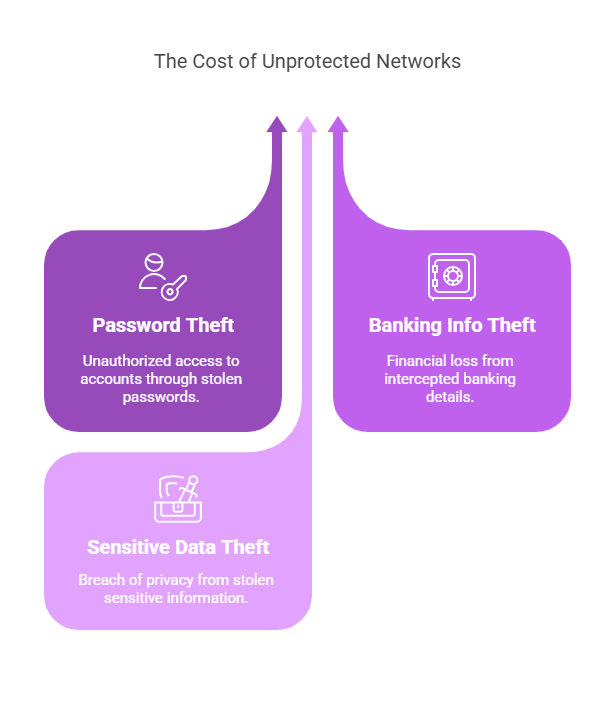
    Risks of an Unprotected Wifi Network

    An unprotected Wi-Fi network is a goldmine for cybercriminals. It allows them easy access to intercept and steal personal data transmitted over the network. Common risks include the theft of passwords, banking information, and other sensitive data that can lead to financial and reputational damage.

    Moreover, without security measures like changing the default username and password, your network can be used to distribute malware or launch attacks on other networks, implicating you in cybercrimes. Therefore, securing your home Wi-Fi network is not just about protecting your internet connection; it’s about safeguarding your entire digital life.

    The Role of Wi-Fi Security in Protecting Personal Information

    Wi-Fi security plays a crucial role in protecting personal data from cyber threats. With the increasing amount of sensitive information being transmitted over Wi-Fi networks, ensuring that your network is secure is more important than ever. Proper security measures prevent unauthorized access and ensure that your personal data remains confidential and safe from potential cyber-attacks.

    By implementing strong Wi-Fi security protocols, you create a barrier that shields your personal information from hackers and cybercriminals. This protection is vital in preventing identity theft, financial fraud, and the unauthorized use of your personal data, maintaining your privacy and security in the digital realm.

    1. Enhance Your Encryption Settings
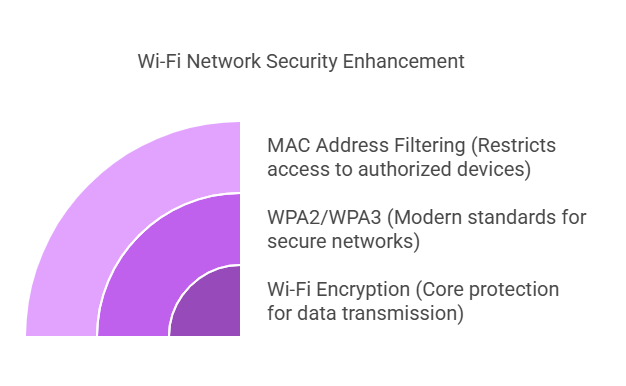
    Enhance your encryption settings.

    Enhancing your encryption settings is a fundamental step in securing your Wi-Fi network. Modern wi-fi routers come with options for encryption, such as WPA2 or WPA3, which safeguard your network by encrypting the data transmitted over it. Additionally, incorporating MAC address filtering adds an extra layer of security, ensuring only authorized devices can connect to your network.

    Switching to WPA3 for Optimal Protection

    WPA3 represents the latest advancement in network security, providing a more robust wireless security protocol than its predecessors. It offers enhanced protection against common cyber threats, ensuring that your Wi-Fi network remains secure against potential attacks. Upgrading to WPA3 is a critical step in fortifying your network’s defenses.

    Why WPA2 or WPA3 with AES Beats Other Encryption Methods

    WPA2 and WPA3 with AES are considered the gold standard for Wi-Fi encryption. They provide a high level of security by encrypting network traffic, which makes it extremely difficult for hackers to intercept or decipher the data transmitted over your Wi-Fi signal. This level of encryption is crucial for protecting sensitive information against cyber threats.

    Compared to older methods like WEP encryption, WPA2 and WPA3 with AES offer significantly improved security features. WEP encryption is outdated and easily cracked by modern hackers, making it inadequate for today’s security needs. Therefore, using WPA2 or WPA3 with AES is essential for maintaining a secure Wi-Fi network.

    The Pitfalls of Using the Wrong Wi-Fi Encryption

    Using outdated or weak Wi-Fi encryption can leave your network vulnerable to attacks. Hackers can easily exploit these vulnerabilities to gain unauthorized access to your network and intercept the data from connected devices. This exposure can lead to data breaches and compromise personal and sensitive information.

    Turning Off WPS for Increased Security

    While the Wi-Fi Protected Setup (WPS) feature offers convenience, it also presents a significant security risk. WPS vulnerabilities can be exploited by attackers to gain unauthorized access to your network. Disabling WPS enhances your network security by eliminating this potential entry point for hackers.

    By turning off WPS, you force all devices to connect through more secure methods, requiring a network security key or the use of a wireless security protocol. This step greatly reduces the risk of unauthorized access, ensuring your network remains protected against potential security breaches.

    2. Update Your Network Regularly
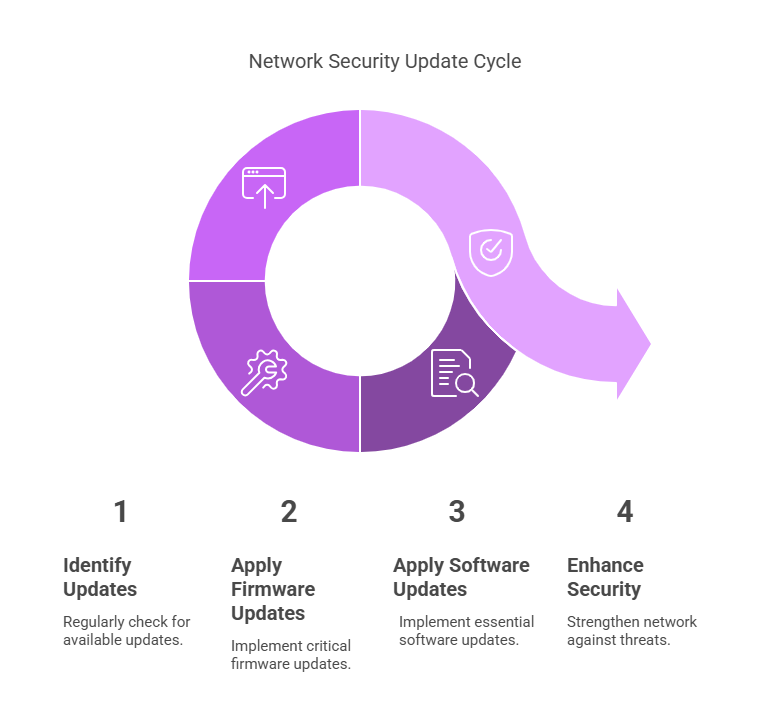
    Update Your Network Regularly

    Regularly updating your network is crucial for maintaining its security. Firmware updates and software updates often contain critical security enhancements that protect your network against new threats. Ensuring these updates are applied promptly is key to safeguarding your network’s integrity.

    The Critical Role of Firmware Updates

    Firmware updates play a vital role in keeping wi-fi routers secure. Manufacturers release these updates to patch vulnerabilities and enhance the router’s security features. Setting your router to automatically update ensures you’re always protected against the latest threats without having to manually check for updates.

    How Regular Updates Prevent Security Breaches

    Applying firmware updates regularly is essential for preventing security breaches. These updates fix vulnerabilities that could be exploited by hackers to gain unauthorized access to your network. By enabling your router to automatically update, you ensure your network benefits from the latest security enhancements, minimizing the risk of cyber-attacks.

    Automatically updating your router not only simplifies the maintenance of your network’s security but also ensures that your defenses are up-to-date. This proactive approach is crucial for protecting against emerging threats and keeping your network secure.

    Custom DNS Servers: A Layer of Extra Security

    Using custom DNS servers adds an extra layer of network security. By choosing a DNS server beyond your ISP, you can gain additional security features, such as phishing protection and content filtering, which enhance your network’s overall security posture.

    Choosing the Right DNS Server Beyond Your ISP

    Selecting the right DNS server is crucial for enhancing your network security. Some DNS servers offer advanced security features that protect against phishing attacks and block access to malicious sites. These features add an additional layer of security, helping to safeguard your network against a wide range of cyber threats.

    Moreover, by choosing a DNS server that prioritizes privacy and does not log your internet activity, you can further protect your online privacy. This consideration is especially important in today’s digital age, where data privacy is a significant concern. Making an informed choice about your DNS server can significantly enhance your network’s security and privacy.

    3. Disable Features that Compromise Security
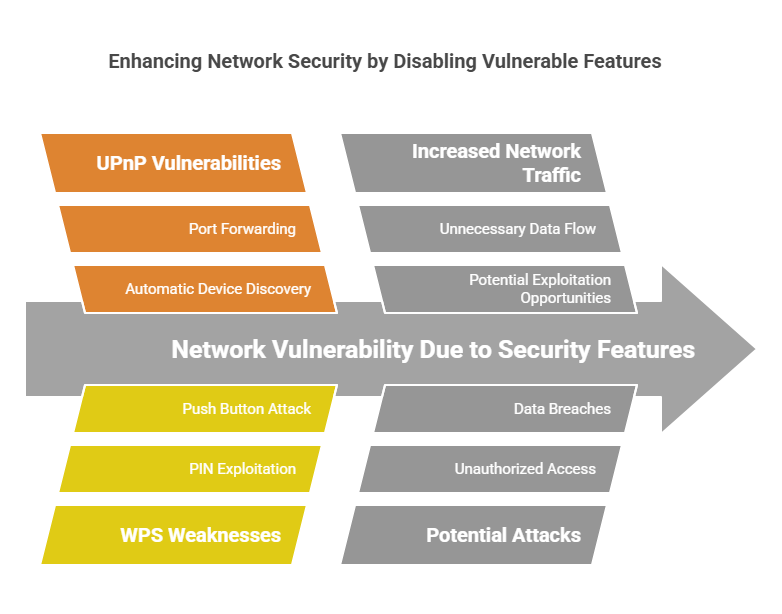
    Disable Features That Compromise Security

    Disabling features that compromise security is essential for maintaining a secure network. Features like UPnP (Universal Plug and Play) and WPS (Wi-Fi Protected Setup) can make your network more vulnerable to attacks. By turning these features off, you reduce unnecessary network traffic that could be exploited by malicious actors, safeguarding your network’s integrity.

    Turning Off UPnP and NAT-PMP to Close Unnecessary Ports

    Universal Plug and Play (UPnP) and Network Address Translation Port Mapping Protocol (NAT-PMP) are features that make it easier for devices to communicate over a network by opening ports automatically. However, this convenience can also be a security risk. By automatically opening ports, they can potentially allow unauthorized devices and potential attackers to gain access to your network. Turning off UPnP and NAT-PMP in your wireless router’s settings helps close these unnecessary ports and secure your router’s configuration.

    The Security Nightmare of Open Ports

    Open ports can be a security nightmare because they act as gateways for potential attackers to enter your network. Network Address Translation (NAT) helps mask your internal network addresses, but when ports are left open, it can provide a direct path for attackers. This vulnerability can compromise the privacy and integrity of your network, leading to unauthorized access and data breaches.

    To mitigate this risk, it’s crucial to manage which ports are open and to understand the purpose of each. Regularly auditing your port status and ensuring that only necessary ports are open for your network’s operation can greatly reduce the risk of cyber threats. This proactive approach to network security can save you from potential data loss and privacy violations.

    The Need to Disable Remote Access

    Remote access allows users to connect to the network from different locations, but it can also be a doorway for attackers to infiltrate your network. Disabling remote access features on your router ensures that control over your network remains strictly within your local environment. This step is essential in protecting your network from unauthorized access and securing your personal information.

    Limiting Administration Access to Your Local Network Only

    Limiting administration access to your local network enhances your security by ensuring that only users within your network can make changes to the router’s configuration. This prevents external attackers from modifying your network settings or installing malicious software. By restricting access to the network’s administration interface to local connections only, you significantly reduce the risk of external breaches.

    Furthermore, implementing strong, unique passwords for router access and changing these passwords regularly can fortify your network against unauthorized attempts to gain entry. Combining these measures with disabling remote access complements your network’s security framework, making it challenging for potential attackers to breach your system.

    4. Create a Separate Network for Guests
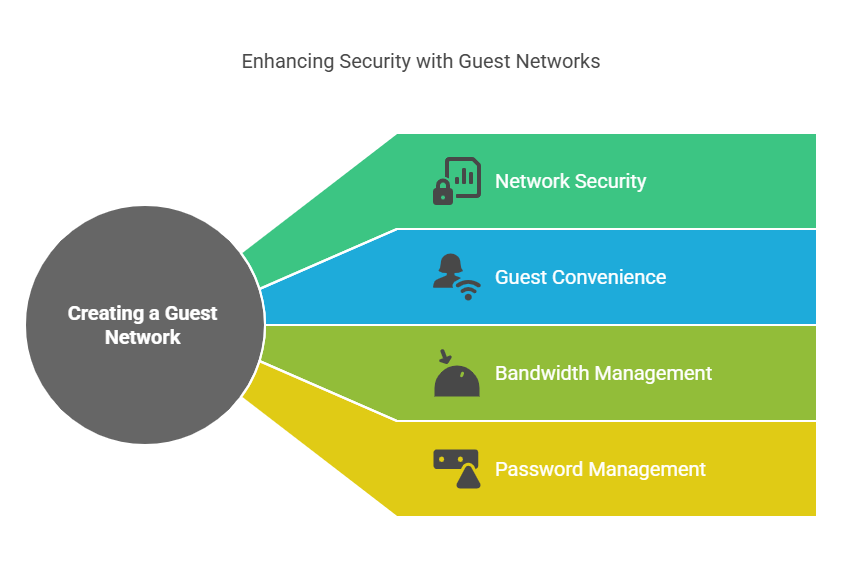
    Create Seperate Guest Network

    Creating a separate network for guests is a strategic move for enhancing network security. A guest network allows visitors to access the internet without compromising the security of the main network. This segregation ensures that your personal devices and sensitive information remain protected from potential threats that guest devices might carry.

    This approach not only secures your primary network but also provides a courtesy to guests by offering them internet access. Adjusting the settings to limit bandwidth on the guest network can prevent it from slowing down your main network. Regularly changing the guest network’s password also maintains a high level of security.

    The Benefits of a Guest Network

    A guest network is beneficial because it isolates guest devices from your main network, ensuring that your personal and business data remain secure. It acts as a barrier that prevents guests from accessing your network’s shared files, printers, and other devices. Providing internet access to visitors without compromising the integrity of your network enhances security while being hospitable.

    Isolating Untrusted Devices to Protect Your Main Network

    Isolating untrusted devices on a guest network safeguards your main network against potential threats. This separation ensures that any malware or security threats present on guest devices do not affect your network’s devices. It’s a proactive step towards maintaining the health and security of your primary network.

    Moreover, implementing a guest network allows for better control and monitoring of network access. You can set restrictions and monitor usage on the guest network without impacting the functionality of your main network. This level of control is crucial in preventing unauthorized access and protecting sensitive information.

    5. Adopt Advanced Security Measures
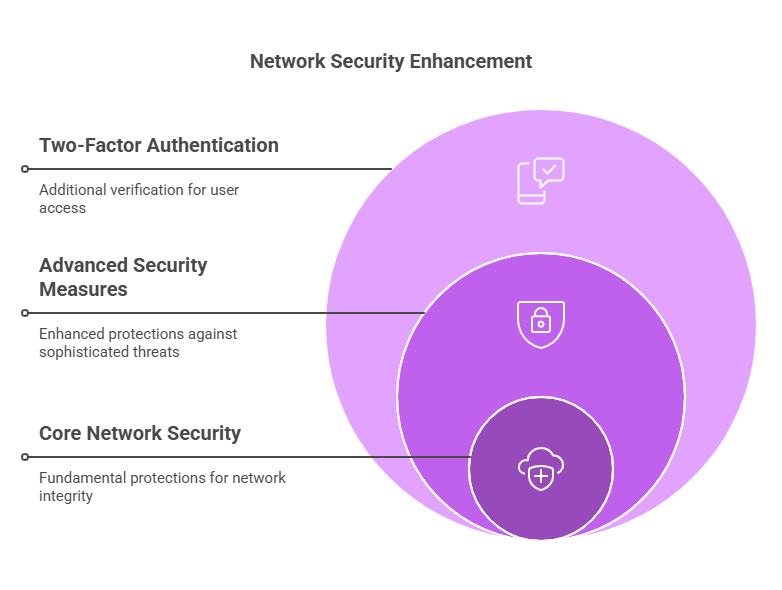
    Adopt Advanced Security Measures

    Adopting advanced security measures is crucial in today’s digital age to protect your network against sophisticated threats. Network security is a critical aspect that requires continuous attention and enhancement. By implementing additional security layers, you can safeguard your network from unauthorized access and ensure the confidentiality, integrity, and availability of your data.

    Implementing Two-Factor Authentication (2FA)

    Implementing Two-Factor Authentication (2FA) adds an extra layer of security to your network. This method requires users to provide two different types of information before gaining access to the network. By adding this additional verification step, it becomes much harder for unauthorized users to compromise your network’s security.

    How 2FA Adds an Extra Layer of Security

    Two-Factor Authentication (2FA) significantly enhances network security by requiring a second form of verification beyond just a password. This could be a text message code, an email, or an authentication app approval. With 2FA, even if a password is compromised, the chances of an unauthorized user gaining access to the network are greatly reduced.

    The implementation of 2FA acts as a deterrent against potential attackers. It’s an effective way to protect sensitive data and network resources from being exploited. For businesses and individuals alike, adopting 2FA is a smart step towards fortifying their network security posture.

    The Necessity of Using Strong, Unique Passwords

    Using strong, unique passwords is fundamental to network security. A robust password acts as the first line of defense in preventing unauthorized access. Changing the default passwords and using a unique identifier for your network is essential. It helps in protecting the network from hackers attempting to connect to the network. Employing complex passwords that are difficult to guess ensures that your network remains secure from potential intrusions.

    Password Management Tips for Enhanced Security

    Effective network security begins with strong password management. Regular firmware updates and changing the security settings are critical steps in safeguarding your network. For all devices that connect to your network, ensure that each has a unique, complex password. This reduces the risk of unauthorized access and enhances your overall security posture.

    Additionally, employing a password manager can help in generating and storing strong passwords for various devices and services. This tool can significantly improve your network security by ensuring that passwords are both strong and unique across all access points. Keeping your network’s firmware updated also plays a crucial role in protecting against vulnerabilities that attackers might exploit.

    Proactive Steps Towards Secure Wi-Fi Use

    Securing your home Wi-Fi network involves several proactive steps. Changing the default password and default username and password is the first critical step. Enabling WPA2 or WPA3 encryption scrambles the information sent over your network, making it harder for outsiders to intercept. Ensuring your router’s firewall is turned on adds another layer of protection against potential cyber threats.

    Avoiding the use of public Wi-Fi networks without a VPN encrypts your data, protecting it from eavesdroppers. For devices like your phone or tablet, regularly updating the router software can prevent security loopholes. These measures, along with disabling Wi-Fi Protected Setup (WPS) and remote access when not needed, play a vital role in protecting your home Wi-Fi network from unauthorized access.

    The Importance of a Comprehensive Wi-Fi Security Strategy

    A comprehensive Wi-Fi security strategy is essential in safeguarding against cyber threats and ensuring the integrity of your network. It involves a multi-layered approach that combines technical measures, such as encryption and firewalls, with user education on best practices. Keeping informed about the latest security risks and regularly updating your network’s defenses are critical components of a robust security strategy.

    By adopting a holistic approach to Wi-Fi security, you can protect not only your personal and financial information but also the devices connected to your network. This proactive stance helps in preventing unauthorized access and securing your digital footprint against potential cyber attacks.

    Educating Users on Wi-Fi Security Best Practices

    Educating users about Wi-Fi security best practices is key to maintaining a secure network. Awareness of potential cyber threats and knowledge of how to avoid them can significantly reduce the risk of security breaches. Users should be informed about the dangers of connecting to unknown networks and the importance of using secure websites.

    Additionally, updating older devices and ensuring they have the latest security patches is crucial for network integrity. Teaching users to recognize phishing attempts and to secure their devices with strong passwords can greatly enhance a network’s defense against malicious activities. Education is a powerful tool in the fight against cyber threats, making it an indispensable part of a comprehensive Wi-Fi security strategy.

    Safeguarding Against Future Threats

    As technology advances, so do the methods employed by cyber criminals to exploit Wi-Fi networks. Staying ahead of these threats requires a proactive approach, focusing on both current and future risks. By understanding the landscape of digital threats, individuals and organizations can better prepare their defenses against unauthorized access and data breaches. This forward-thinking strategy is crucial for maintaining the integrity and security of Wi-Fi networks.

    Part of safeguarding against future threats involves embracing new technologies and security protocols. The adoption of encrypted DNS and more sophisticated encryption methods plays a pivotal role in this process. Additionally, forming technology alliances and participating in cybersecurity communities can provide valuable insights into emerging risks and the latest defensive tactics. These collective efforts contribute significantly to the resilience of network security, ensuring that Wi-Fi users can navigate the digital world more safely.

    Staying Informed About Emerging Wi-Fi Security Risks

    With cyber criminals constantly evolving their tactics, it is vital to stay informed about new Wi-Fi security risks. This involves keeping up to date with the latest security research, as well as any reported breaches or exploits. Awareness of these risks allows users and administrators to adjust their security measures accordingly, minimizing the potential for unauthorized access. Regularly consulting reputable security news sources and attending cybersecurity conferences can help in staying ahead of potential threats.

    Implementing a strategy that includes monitoring the security landscape helps in identifying vulnerabilities within a Wi-Fi network before they can be exploited. This proactive approach to security not only protects sensitive information but also preserves the trust of those who rely on the network. By staying informed, users can implement timely updates and refine their security practices, further fortifying their defenses against emerging threats.

    The Role of Technology Alliances in Strengthening Network Security

    Technology alliances play a critical role in bolstering Wi-Fi security across the board. These collaborations between technology companies, security experts, and regulatory bodies lead to the development of more robust security standards and practices. By sharing knowledge and resources, members of these alliances can collectively address vulnerabilities and enhance the overall security of Wi-Fi networks. This cooperative effort is essential for staying ahead of cyber criminals and safeguarding digital information.

    Such alliances also facilitate the rapid dissemination of information regarding new threats and vulnerabilities, enabling quicker responses to potential security breaches. Furthermore, they often contribute to the development of new security technologies and protocols, such as encrypted DNS, which can significantly improve the security of Wi-Fi networks. Through these partnerships, the digital community benefits from a unified front against cyber threats, making the internet a safer place for everyone.

    The Ongoing Journey of Wi-Fi Security

    The landscape of Wi-Fi security is ever-changing, with new challenges and solutions emerging regularly. This ongoing journey requires constant vigilance and adaptation to ensure networks remain secure. As methods of unauthorized access evolve, so too must the strategies employed to prevent them. This dynamic environment demands that individuals and organizations remain committed to strengthening their Wi-Fi security over time, adapting to the latest threats and employing the most effective defenses available.

    Part of this evolutionary process involves learning from past security incidents and integrating those lessons into future security planning. This iterative approach helps in refining and enhancing Wi-Fi security measures, ensuring they are capable of protecting against both current and future threats. The journey of Wi-Fi security is one of continuous improvement, with each step forward making the digital world a safer place to connect and share.

    The Evolution of Wi-Fi Security Measures

    Wi-Fi security has seen significant advancements since its inception, evolving from simple password protection to sophisticated encryption methods. This evolution has been driven by the need to protect against unauthorized access and ensure the privacy of users. As cyber criminals have developed more complex methods of attack, Wi-Fi security measures have similarly advanced. This includes the implementation of stronger encryption methods, the use of MAC addresses filtering, and the adoption of technologies designed to secure Apple devices and other IP addresses.

    The shift towards more advanced security measures reflects the growing understanding of the complexities involved in protecting Wi-Fi networks. Recognizing the limitations of early security protocols, developers and security experts have worked diligently to introduce more robust solutions, such as encrypted DNS. These advancements not only provide stronger protection against cyber threats but also serve as a testament to the ongoing commitment to enhance Wi-Fi security. As technology continues to progress, so too will the methods used to safeguard digital networks and the information they transmit.

    The Continuous Need for Vigilance and Updates

    The fight against cyber threats is an ongoing battle that requires continuous vigilance and regular updates. Cyber criminals are persistently finding new ways to breach networks, making it essential for Wi-Fi security measures to evolve in response. This includes the need to automatically install updates to ensure that security software and firmware are equipped with the latest defenses against potential attacks. By keeping systems up to date, users can protect themselves from vulnerabilities that could be exploited by attackers.

    Additionally, the adoption of automated security protocols, such as SSID broadcast disabling and controls over which devices are allowed to connect, further enhances network security. Employing strong data protection practices, including the use of robust encryption methods that encrypt data, is crucial for defending against cyber criminals. These steps, combined with ongoing education on security best practices, form the cornerstone of a comprehensive strategy to maintain Wi-Fi security. The continuous need for vigilance and updates is paramount in ensuring that networks remain secure in the face of evolving threats.

    Some of our wireless solutions providers are listed here.

    Contact Us For More Information
  • Email Security Service: Your Ultimate Guide to Protection

    Email Security Service: Your Ultimate Guide to Protection

    Email Security Service: Your Ultimate Guide to Protection

    In an era where digital correspondence forms the backbone of corporate communication, securing one’s email ecosystem has transcended beyond a mere recommendation to an absolute necessity. With cyber threats evolving at an unprecedented rate, organizations are finding themselves in a constant battle against schemes aimed at data exfiltration, making the adoption of robust email security services a critical step towards safeguarding sensitive information.

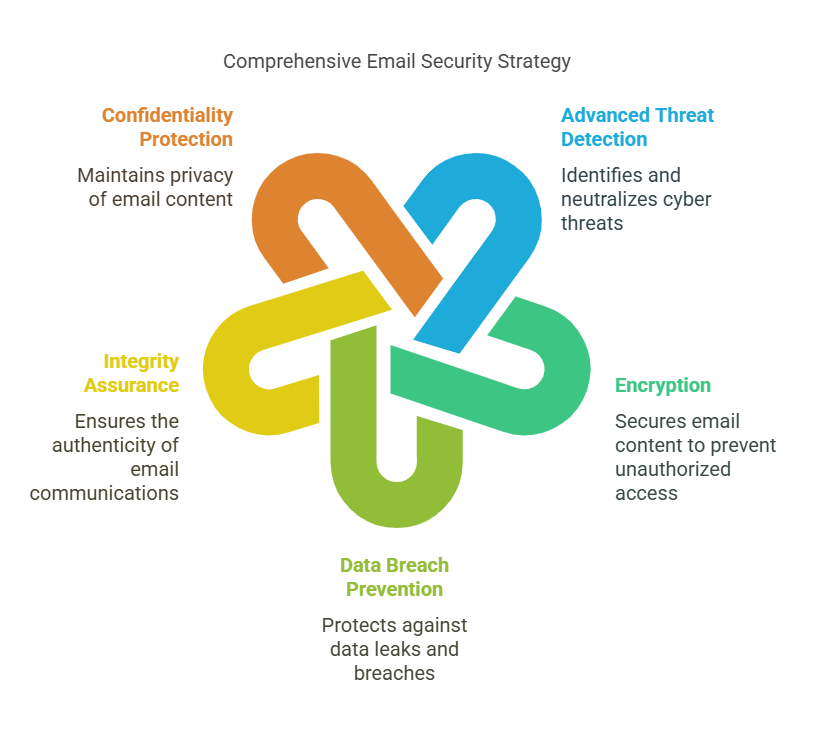
    This type of security service is designed to offer a multifaceted protection strategy, encompassing everything from advanced threat detection to encryption, in order to combat the sophisticated tactics employed by cybercriminals. Recognizing the dire consequences of data breaches, businesses are now prioritizing the integration of these services to ensure the integrity and confidentiality of their email communications.

    Understanding the Essentials of Email Security Services

    Email Security Service Your Ultimate Guide to Protection

    At its core, an email security service is engineered to protect against a wide range of cyber threats, including the perilous act of data exfiltration. Through a combination of cutting-edge technologies and strategic protocols, these services strive to fortify email systems against unauthorized access and misuse.

    The Increasing Importance of Email Security Solutions

    As the digital landscape becomes increasingly perilous, the importance of email security solutions cannot be overstated. With email being a primary vector for cyberattacks, businesses and individuals alike are facing heightened risks of data breaches, identity theft, and financial loss. In response, the demand for comprehensive email security solutions that can effectively thwart these risks has skyrocketed, highlighting the crucial role these defenses play in today’s cybersecurity ecosystem.

    Key Features That Define Top-Notch Email Security

    Advanced Threat Prevention Techniques

    Top-tier email security encompasses advanced threat prevention techniques, leveraging AI-powered protection to offer real-time threat detection. This approach allows for the identification and neutralization of advanced threats before they can infiltrate the network, underscoring the pivotal role of innovative technology in contemporary cybersecurity measures.

    Email Encryption: A Non-Negotiable for Data Protection

    Email encryption stands as a cornerstone of data security, ensuring that sensitive information remains inaccessible to unauthorized parties. In conjunction with security policies and content filtering, encryption addresses the stringent regulatory requirements governing data protection, thereby playing a crucial role in the defense against data breaches and cyber espionage.

    Comprehensive Phishing and Malware Defense

    The relentless rise in phishing emails and malware necessitates a comprehensive defense strategy, integrating sophisticated malware detection systems to scrutinize incoming messages for malicious intent. By effectively identifying and blocking these threats, businesses can significantly reduce their vulnerability to cyberattacks, safeguarding their assets and reputation.

    Incident Response: Preparing for When Things Go Wrong

    Despite the most robust defenses, incidents can occur, making a well-prepared incident response plan an indispensable component of email security. This plan ensures that, in the event of a breach, measures are promptly taken to mitigate damage, assess system vulnerabilities, and restore normal operations, thereby minimizing the impact on the organization.

    Comprehensive Solutions for Email Threat Prevention

    Addressing the multifaceted nature of email threats requires a comprehensive solution that integrates advanced threats detection, AI-powered protection, and real-time threat detection. This holistic approach is critical for organizations aiming to maintain a secure and resilient email ecosystem amidst the evolving cyber threat landscape.

    AI-Powered Email Security Services: Beyond Traditional Defenses

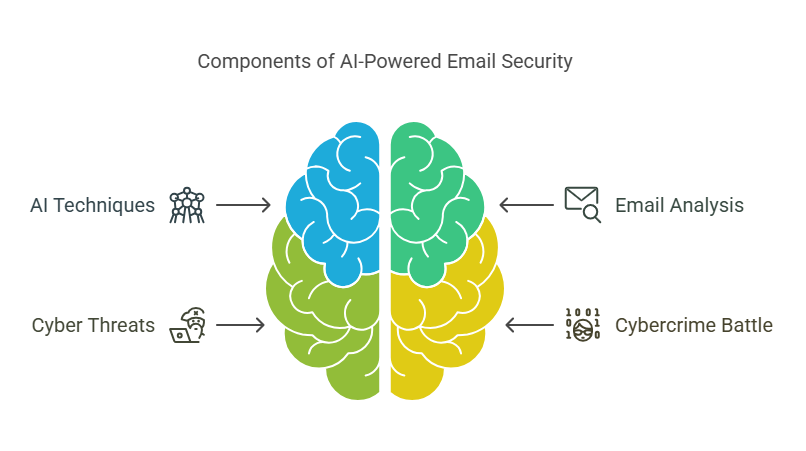
    AI Powered Email Security Services

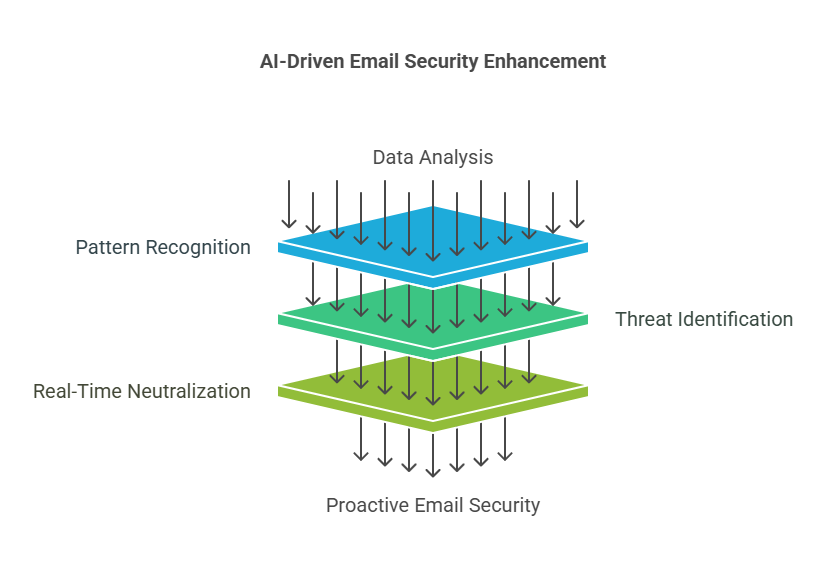
    AI-powered services offer a significant advancement over traditional defenses, employing sophisticated email analysis techniques powered by artificial intelligence. These systems are adept at identifying and neutralizing even the most cunning cyber threats, representing a quantum leap forward in the ongoing battle against cybercrime.

    The Role of Secure Email Gateways in Modern Cybersecurity

    Secure email gateways serve as a critical bulwark in modern cybersecurity strategies, filtering incoming email traffic to remove spam, malicious content, and other undesired communications. By scrutinizing every message that enters the network, these gateways play a pivotal role in maintaining the integrity and security of email communications.

    Cloud-Based vs. AI-Enhanced Email Security: A Comparative Overview

    In the realm of email security, both cloud-based and AI-enhanced solutions offer distinct advantages in combating malicious messages. The choice between them hinges on specific organizational needs, including scalability, real-time defense capabilities, and the sophistication of threats faced.

    The Flexibility and Scalability of Cloud-Based Solutions

    Cloud-based email security solutions are celebrated for their flexibility and scalability, accommodating the dynamic needs of email systems amid evolving threats. These solutions not only provide robust defense against email-based attacks but also ensure that security measures grow in tandem with the organization.

    The Advanced BEC Defense Offered by AI-Enhanced Services

    AI-enhanced email security services excel in defending against Business Email Compromise (BEC) attacks, utilizing cutting-edge technology to identify and neutralize sophisticated schemes. By analyzing communication patterns and identifying anomalies, these services offer an unparalleled level of protection against one of the most insidious threats in today’s cybersecurity landscape.

    Navigating Through Types of Email Security Services

    In the diverse ecosystem of email security services, organizations are confronted with a range of options designed to mitigate potentially malicious activities and protect against malicious emails. Understanding the nuances of these services is essential for selecting the solution that best aligns with specific security requirements and threat landscapes.

    From Secure Email Gateways to API-Based Protection

    The transition from traditional secure email gateways to API-based protection represents a significant evolution in the fight against cyber threats. Secure email gateways have long been the bulwark against spam filtering and malicious content, diligently monitoring email traffic to safeguard users. However, API-based protection has emerged as a more dynamic solution, offering real-time, automated defenses that adapt to the constantly evolving landscape of email-based threats. This approach not only enhances the ability to detect sophisticated phishing attempts but also ensures a more granular control over email security, catering to the specific needs of modern organizations.

    Email Data Protection (EDP) and Its Significance

    Email Data Protection

    Email Data Protection (EDP) is critical in today’s digital age, where data breaches are increasingly common. EDP safeguards sensitive information by enforcing security policies, content filtering, and meeting regulatory requirements. This ensures that an organization’s email communications are secure, protecting against data leaks and unauthorized access. Furthermore, EDP plays a pivotal role in maintaining data security, crucial for compliance and preserving client trust. By implementing EDP, businesses can significantly mitigate the risk of data exposure and enhance their overall security posture.

    The Evolution and Impact of Email Encryption Services

    Email encryption services have undergone significant evolution, transforming from simple, optional tools into essential components of email security strategies. This evolution reflects the growing awareness of the risks associated with unsecured email communications. Today, email encryption not only secures the contents of an email but also verifies the identity of the sender, ensuring that sensitive information remains confidential and tamper-proof during transit. The impact of these services has been profound, significantly reducing the incidence of data breaches and enhancing privacy in digital communications.

    Why API-Based Email Security Solutions Stand Out

    API-based email security solutions stand out for their flexibility and ability to seamlessly integrate with existing email infrastructures. Unlike traditional methods that act as external barriers, API-based solutions work from within, offering a more nuanced approach to detecting suspicious emails and phishing attempts. This allows for real-time scanning of email content, providing immediate protection without the latency associated with traditional security measures. The direct integration with existing email systems enables a more comprehensive and effective defense mechanism, setting API-based solutions apart in the realm of email security.

    Deployment and Integration: Making the Right Choice

    Choosing the right deployment and integration strategy for an email security solution is paramount. It requires a delicate balance between robust security measures, such as advanced email security and real-time scanning, and the need to meet compliance requirements. The right solution must seamlessly mesh with existing email systems, ensuring that phishing attempts and suspicious emails are intercepted without disrupting the flow of legitimate communications. This balance is crucial for maintaining an optimal level of security while also ensuring the smooth operation of business communications.

    Evaluating Your Email Security Service Deployment Options

    When evaluating email security service deployment options, organizations must consider the nature of their email traffic and the specific threats they face. The decision between on-premises, cloud-based, or hybrid solutions depends on various factors, including the need for scalability, control over data sovereignty, and the ability to protect against advanced email security threats. Each option presents its own set of advantages and challenges, making it essential for businesses to assess their unique requirements and security goals before making a decision. This careful evaluation ensures that the chosen solution aligns with the organization’s overall cybersecurity strategy.

    Ensuring Seamless Integration With Your Existing Tech Stack

    Seamless integration with the existing tech stack is crucial when implementing a new email security solution. Security vendors play a pivotal role in this process, offering tools and services designed to complement and enhance existing systems. The goal is to create a cohesive security environment where new and existing solutions work in harmony, minimizing compatibility issues and ensuring efficient operation. This not only streamlines the security management process but also maximizes the effectiveness of the overall cybersecurity framework, safeguarding against emerging threats without adding undue complexity.

    Reviewing Compliance Requirements: A Critical Step

    Reviewing compliance requirements is a critical step in selecting an email security solution. Every industry faces unique regulatory demands, from healthcare’s HIPAA to the financial sector’s GLBA. A comprehensive email service must not only protect against cyber threats but also ensure that all communications comply with these stringent requirements. Failure to do so can result in severe penalties and loss of reputation. Therefore, businesses must diligently assess their compliance needs and choose solutions that offer robust security while adhering to relevant regulations.

    Assessing the Resources Needed for Optimal Operation

    Assessing the resources needed for the optimal operation of an email security system is vital for its success. This includes evaluating the human, technological, and financial resources required to maintain and manage the system effectively. Organizations must consider the expertise of their security teams, the compatibility of the new system with existing infrastructure, and the budgetary constraints that may impact the choice of solution. A thorough assessment ensures that the selected email security service not only meets the organization’s security needs but is also sustainable and effective in the long term.

    Selecting the Right Email Security Service for Your Needs

    Selecting the right email security service requires a nuanced understanding of the organization’s specific needs and challenges. This involves considering factors such as the volume and nature of existing email traffic, the sophistication of potential phishing attempts, and the need for advanced email security features like real-time scanning. A tailored approach ensures that the chosen solution effectively addresses the unique threats faced by the organization, providing comprehensive protection against suspicious emails and other cyber threats without compromising the efficiency of email communications.

    Keys to Choosing an Effective Email Security Solution

    Choosing an effective email security solution hinges on several key factors. These include the ability to detect and neutralize phishing attempts, the integration capabilities with existing email systems, and the provision of real-time scanning for suspicious emails. Additionally, the solution should offer advanced email security features that can adapt to evolving cyber threats. Organizations must carefully evaluate these criteria to ensure that their chosen email security solution not only meets their current security needs but is also scalable for future requirements.

    Discovering the Right Email Security Plan for Your Industry

    Discovering the right email security plan requires an in-depth understanding of the specific threats and regulatory requirements pertinent to one’s industry. This involves a careful assessment of the types of cyber threats most commonly faced, such as phishing attacks or advanced malware, and the level of data protection required by industry standards. By aligning the email security solution with these industry-specific needs, organizations can ensure robust protection against targeted attacks, safeguarding their sensitive data and maintaining compliance with regulatory mandates.

    Frequently Asked Questions About Email Security Services

    Frequently asked questions about email security services often revolve around their ability to offer comprehensive protection against a wide range of cyber attacks. Queries may include the effectiveness of AI-powered email security in preventing email-borne attacks, the role of managed XDR in enhancing protection, and how security awareness training can bolster defenses. Additionally, questions may delve into the capabilities of advanced algorithms and malware protection in identifying and neutralizing threats. Addressing these questions helps demystify the complex landscape of email security, guiding organizations in their quest for robust cybersecurity solutions.

    The Definitive Guide to Understanding Advanced Email Protection

    Understanding advanced email protection involves grasping the nuances of combating cyber threats through sophisticated means such as advanced threat protection and email threat protection solutions. These technologies are designed to identify and mitigate not only known threats but also unknown threats that conventional security measures may overlook. A comprehensive protection solution integrates these advanced mechanisms to provide a robust defense against the ever-evolving landscape of cyber threats, ensuring the security of digital communications.

    How AI and Machine Learning Are Revolutionizing Email Security

    AI and Machine Learning Are Revolutionizing Email Security

    AI and machine learning are revolutionizing email security by enhancing anti-phishing capabilities, allowing for the identification and neutralization of threats in real-time. These technologies learn from vast quantities of data to recognize patterns associated with phishing attempts and other malicious activities. By continuously adapting to new threats, AI and machine learning ensure that email security systems remain at the forefront of cyber defense, providing dynamic, proactive protection against the sophisticated tactics employed by cybercriminals.

    The Importance of Advanced BEC Defense in Today’s Cyber Landscape

    In the digital age, the sophistication of cyber threats, particularly Business Email Compromise (BEC), has elevated the need for advanced defense mechanisms. BEC attacks, which often involve the impersonation of executives or trusted partners, can lead to significant financial losses and data breaches. The complexity of these schemes means traditional security measures are often insufficient, necessitating a shift towards more nuanced and intelligent solutions capable of identifying and mitigating such targeted threats before they can cause harm.

    Crafting a Definitive Email Cybersecurity Strategy Guide

    Developing a robust email cybersecurity strategy is imperative for organizations to protect themselves against an ever-evolving threat landscape. This strategy should encompass a comprehensive approach, including the deployment of cutting-edge technologies for detecting phishing, implementing stringent access controls, and educating employees on the importance of cybersecurity hygiene. By adopting a multi-layered defense mechanism, organizations can significantly reduce their vulnerability to malicious attacks, ensuring the integrity and confidentiality of their email communications.

    Essential Steps to Fortify Your Email Security Posture

    Strengthening your email security posture involves a series of critical steps, beginning with a thorough assessment of current vulnerabilities and potential cyber threats. This process includes the adoption of advanced anti-phishing tools and regular security audits to identify and rectify weaknesses in the system. Additionally, implementing robust data protection policies and ensuring that all users are aware of best practices for email security can dramatically reduce the risk of malware attacks and other cyber threats, safeguarding sensitive information from unauthorized access.

    Best Practices for Preventing Email Attacks and Ensuring Data Security

    To mitigate the risk of email attacks and enhance data security, organizations should adopt a set of best practices that include the use of advanced anti-phishing solutions and the implementation of strong password policies. Regular training sessions for employees on recognizing and responding to phishing attempts are crucial. Furthermore, the integration of end-to-end encryption for email communications ensures that data remains protected, both in transit and at rest, significantly reducing the likelihood of unauthorized access and ensuring compliance with data protection regulations.

    Conclusion: Elevating Your Email Security With Confidence

    In conclusion, navigating the complex landscape of email security requires a proactive and comprehensive approach. By embracing advanced email security solutions, organizations can protect themselves against email-based threats and targeted attacks. Leveraging the insights from the Forrester Wave on endpoint protection and adopting strategies for detecting phishing, businesses can build a resilient cybersecurity posture that adapts to the evolving nature of threats, ensuring the confidentiality, integrity, and availability of their email communications.

    The Path Forward: Embracing Advanced Email Security Solutions

    The path forward for organizations looking to bolster their defense against sophisticated email threats involves embracing advanced email security solutions. By integrating cutting-edge technologies such as AI and machine learning for detecting phishing and sophisticated threats, businesses can stay ahead of attackers. The adoption of solutions offering impersonation protection and advanced BEC defense is critical. Additionally, the use of cybersecurity platforms that minimize false positives and efficiently scan QR codes for malicious content can significantly enhance an organization’s cybersecurity posture, ensuring robust protection against a wide array of email-based threats.

    Ensuring Peace of Mind in an Era of Sophisticated Email Threats

    At a time that is dominated by sophisticated threats, achieving peace of mind requires a fortified cybersecurity posture that encompasses advanced solutions for protecting against BEC attacks, impersonation, and other email-based threats. The cornerstone of this defense is the deployment of a comprehensive cybersecurity platform that not only defends against sophisticated threats but also enhances the organization’s ability to reduce false positives, ensuring that legitimate communications are not hindered. Through continuous improvement and adoption of cutting-edge technologies, businesses can safeguard their operations from the ever-present risk of cyber attacks, ensuring operational resilience and trustworthiness.

    Our mail, messaging and email security providers are listed here.

    Contact Us For More Information
  • Network Infrastructure Procurement: Strategies for 2025

    Network Infrastructure Procurement: Strategies for 2025

    Network Infrastructure Procurement

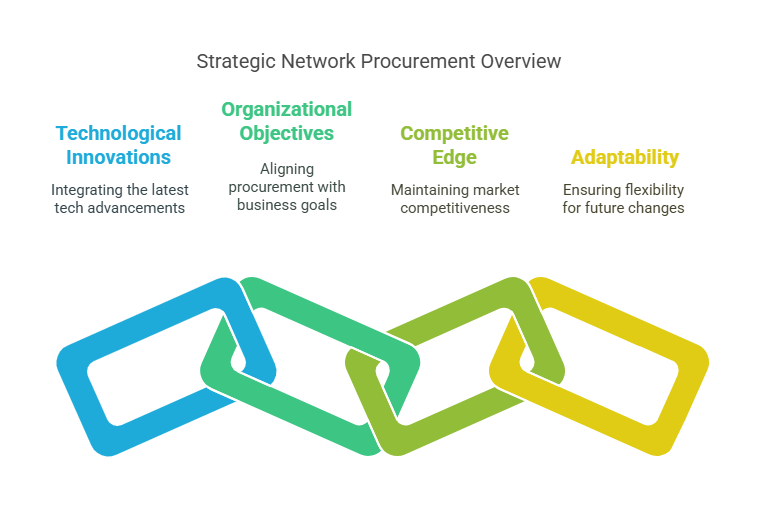
    As businesses navigate the complexities of modern IT requirements, the strategic importance of network infrastructure procurement becomes ever more critical. This process, pivotal for sustaining and scaling operations, demands a forward-thinking approach that integrates the latest technological innovations and aligns closely with organizational objectives. To stay competitive, companies must refine their procurement strategies, ensuring they not only meet immediate needs but are also adaptable to future technological shifts.

    Central to successful procurement is the development of a comprehensive procurement plan that emphasizes the selection of technologies and services which offer scalability, reliability, and security. Evaluation criteria must be meticulously defined to guide procurement decisions, ensuring they contribute to the long-term goals of the organization. Moreover, effective lifecycle management of IT assets is crucial for maximizing their value and performance over time.

    Engaging relevant stakeholders in the procurement process enhances the alignment with business objectives and organizational goals. This collaborative approach ensures that all aspects of the network infrastructure are designed to support the overarching strategic vision of the company. By prioritizing these elements, businesses can achieve a robust network infrastructure that propels them towards their future aspirations.

    Understanding Network Infrastructure Sourcing

    network infrastructure procurement

    At its core, network infrastructure procurement involves a strategic process tailored to secure the technological backbone of an organization. It encompasses a broad range of components, such as hardware, software, and services, essential for creating and maintaining a reliable IT network. A well-crafted procurement plan is vital, integrating evaluation criteria and procurement decisions that resonate with the business objectives and the long-term goals of the company. Project procurement, aligned with these objectives, ensures the seamless integration of new technologies into existing systems, fostering innovation and efficiency across operations.

    The Essence and Scope of Infrastructure Procurement in IT

    The realm of IT infrastructure procurement extends beyond mere purchasing decisions. It encapsulates a strategic framework designed to ensure that every acquisition supports the company’s immediate and future technological needs. This intricate process demands a comprehensive understanding of the current IT landscape, future technological trends, and how these align with the company’s strategic direction. By focusing on these elements, businesses can craft an IT infrastructure that not only meets today’s demands but is also adaptable to tomorrow’s challenges.

    Comparing IT Procurement and General Procurement Practices

    While IT procurement and general procurement share common objectives, the former presents unique challenges and complexities. IT procurement demands a deeper insight into technological trends and their impact on business operations. Unlike general procurement, where the focus might be on cost-effectiveness and supplier reliability, IT procurement emphasizes compatibility, scalability, and security. This distinct focus requires IT procurement professionals to possess a blend of technical knowledge and strategic foresight, enabling them to make informed decisions that align with the organization’s technological roadmap.

    The Role of Digital Procurement in Modern Network Infrastructure

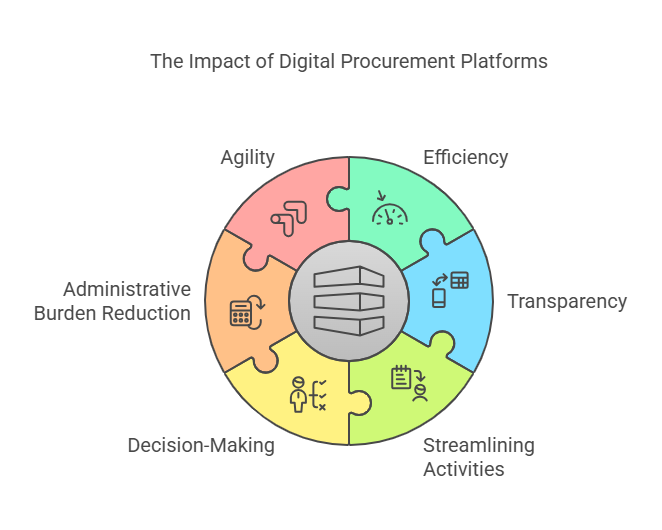
    Digital procurement has emerged as a transformative force in the realm of network infrastructure, streamlining procurement processes and enabling more informed decisions. By leveraging digital platforms, organizations can achieve greater visibility into their procurement activities, from lifecycle management to aligning purchases with strategic business objectives. This digital shift not only enhances efficiency but also empowers businesses to adapt quickly to technological advancements and changing market dynamics.

    How Digital Platforms Are Revolutionizing Procurement Strategies

    Digital platforms are redefining procurement strategies by offering unprecedented access to data and analytics, facilitating informed decisions across the procurement lifecycle. These platforms enable a more agile procurement process, where market trends and vendor capabilities can be analyzed in real time. This shift towards digital procurement not only optimizes operational efficiency but also fosters a more strategic approach to purchasing, ensuring that every investment is fully aligned with the business’s long-term technological aspirations.

    The Strategic Approach to Procurement

    Strategic approach to procurement

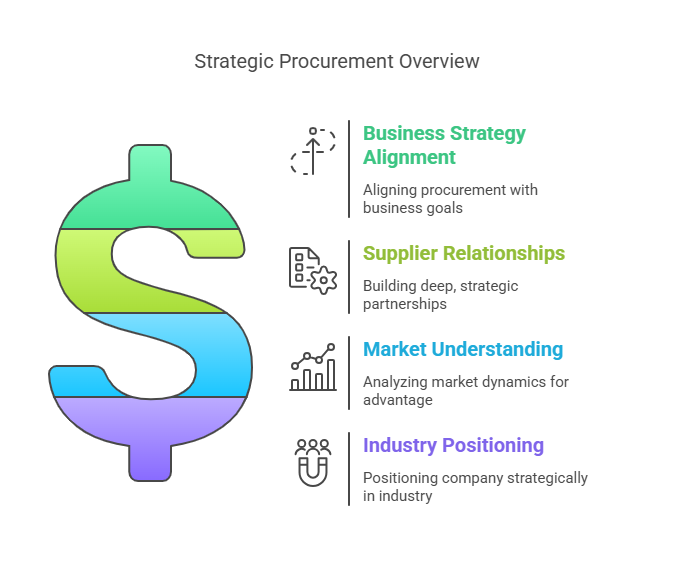
    Adopting a strategic approach to procurement entails a shift from traditional procurement methods towards a more integrated and holistic process. This approach focuses on aligning procurement activities with the overall business strategy, ensuring that procurement contracts contribute positively to the organization’s goals. Effective procurement goes beyond mere transactional relationships with suppliers; it involves a deep understanding of market dynamics and the strategic positioning of the company within its industry.

    Developing a Robust Procurement Strategy

    At the heart of a successful network infrastructure is a robust procurement strategy, one that clearly defines procurement objectives and aligns them with the organization’s strategic vision. This strategy serves as the blueprint for all procurement activities, guiding the selection of technologies and partners that will drive the organization forward. By establishing clear objectives, businesses can navigate the complexities of the IT landscape with precision, ensuring that every procurement decision advances their strategic goals.

    Embracing Cloud Solutions and Central Vendors for Hardware Procurement

    The procurement strategy of the future emphasizes the importance of cloud solutions and the selection of central vendors for hardware procurement. This approach not only simplifies the selection process but also strengthens vendor relationships by fostering collaboration and innovation. By prioritizing vendors that offer comprehensive cloud-based solutions, organizations can achieve greater flexibility and scalability, essential attributes for adapting to the rapidly evolving technological landscape.

    Ensuring Compliance and Leveraging Data Analytics

    A forward-thinking procurement strategy also encompasses ensuring compliance with industry standards and leveraging data analytics for informed decisions. This dual focus allows organizations to navigate the complexities of international deliveries and regulatory requirements with ease. Data analytics, in particular, plays a crucial role in refining procurement strategies, offering insights that drive efficiency and cost-effectiveness across global operations.

    Planning for Scalability, Adaptability, and Distributed Team Support

    Strategic planning for network infrastructure procurement must prioritize scalability, adaptability, and support for distributed teams. This foresight ensures that the infrastructure can accommodate growth and change, facilitating seamless collaboration across geographical boundaries. By anticipating these needs, organizations can build a network that not only meets today’s requirements but is also primed for tomorrow’s challenges.

    Infrastructure Procurement Models: From Traditional to Innovative

    The landscape of infrastructure procurement is evolving, with a shift from traditional delivery models towards innovative approaches that emphasize flexibility and risk management. This transformation reflects the changing needs of businesses in a digital age, where agility and responsiveness are key to staying competitive. By exploring new procurement models, organizations can find solutions that are tailored to their unique challenges and opportunities.

    Public-Private Partnerships and Design, Build, Finance, Operate (DBFO) Models

    Public-private partnerships and Design, Build, Finance, Operate (DBFO) models offer innovative solutions for managing upfront costs and operational risks in infrastructure projects. These models facilitate collaboration between the public and private sectors, leveraging the strengths of each to achieve mutually beneficial outcomes. By distributing the financial and operational responsibilities, these models can deliver high-quality infrastructure solutions that are both efficient and sustainable.

    Exploring Alternative Procurement Models

    In response to the dynamic IT landscape, exploring alternative procurement models has become essential for organizations seeking flexibility and innovation. These models, ranging from crowd-sourced solutions to cooperative procurement agreements, offer fresh perspectives on how to approach the challenges of infrastructure development. By considering these alternatives, organizations can uncover opportunities to optimize costs, enhance efficiency, and drive technological advancement.

    The Procurement Process Explained

    The procurement process is a structured journey from identifying needs to monitoring performance, designed to secure the best possible resources for an organization’s IT infrastructure. This process involves meticulous planning, strategic selection, and ongoing management to ensure that the procurement aligns with the organization’s objectives and delivers value over the long term. By understanding and effectively managing this process, businesses can build a solid foundation for their technological future.

    The Ideal IT Procurement Management Process: A Step-by-Step Guide

    The IT procurement management process is a meticulous journey that demands precision at every turn. It begins with a thorough needs assessment, ensuring that all decisions made are informed and targeted towards the organization’s strategic goals. This stage is critical as it sets the tone for the entire procurement lifecycle, underlining the importance of making informed decisions. Following the assessment, a detailed plan is drafted, outlining the procurement strategy, which includes timelines, budget allocations, and specific technology requirements. The process is highly collaborative, involving key stakeholders to ensure that the procurement strategy aligns with the broader organizational objectives.

    From Needs Assessment to Performance Monitoring

    Transitioning from needs assessment to performance monitoring encapsulates a series of strategic steps designed to optimize the procurement process. After identifying the specific needs, the procurement team develops a comprehensive strategy, focusing on selecting solutions that offer seamless integration with existing infrastructure while being mindful of financial constraints. The strategy also involves ensuring robust contract management and mitigating risks such as data breaches. Following the selection and implementation of the solution, performance monitoring becomes pivotal. This phase is not only about assessing the operational efficiency but also ensuring that the solution continues to meet the evolving needs of the organization, thereby maximizing the return on investment.

    Key Roles and Responsibilities in the Procurement Ecosystem

    In the procurement ecosystem, each role is a cog in a larger machine, driving efficiency and productivity. Procurement specialists are the architects, designing the procurement strategy while ensuring compliance with regulations and fostering strong relationships with service providers.  Our technical services experts are ideally placed to be able to suggest solutions for problems and areas of expansion for existing infrastructures.  Contract management falls under their purview, requiring a keen eye for detail and a thorough understanding of commercial terms. Meanwhile, project teams focus on the seamless execution of procurement plans, liaising with service delivery units to ensure that the procured solutions meet the specified requirements. In the public sector, the emphasis is also on transparency and accountability, ensuring that procurement activities align with public interest and policy objectives.

    Asset Management and Project Delivery within IT Procurement

    Effective asset management and project delivery are cornerstone elements in IT procurement, especially as they relate to controlling increased costs and ensuring the success of infrastructure projects. Procuring authorities must navigate the complexities of commercial arrangements with a strategic mindset, aiming to secure the best value for their investment. This involves a delicate balance between cost, quality, and long-term asset sustainability, underpinning the success of IT procurement endeavors. The goal is to achieve a seamless integration of new technologies into the existing network infrastructure, enhancing operational capabilities without incurring unnecessary expenses.

    Implementing Effective IT Asset Management Strategies

    To bolster operational efficiency, implementing effective IT asset management strategies is paramount. This involves a systematic approach to managing IT assets throughout their lifecycle, from acquisition to disposal. The strategy should encompass regular reviews of asset performance, ensuring they continue to meet the organization’s needs and adapting to technological advancements. Furthermore, it includes optimizing the use of existing assets, thereby reducing the need for unnecessary procurements and controlling costs. Effective asset management also means being proactive in maintenance, minimizing downtime, and extending the lifespan of assets, contributing significantly to the overall efficiency of IT operations.

    Overcoming Procurement Challenges

    IT procurement is fraught with challenges, from navigating financial constraints to ensuring seamless integration of new solutions with existing infrastructure. The landscape is ever-evolving, demanding that procurement professionals adapt swiftly to maintain competitiveness. A robust procurement strategy becomes their north star, guiding them through the complexities of modern IT procurement, ensuring that each decision made is strategic and informed.

    Common Challenges in IT Procurement

    The path of IT procurement is often beset by hurdles such as financial constraints, the need for seamless integration with existing infrastructure, and the looming threat of data breaches. For procurement professionals, the challenge involves ensuring that each step of the procurement process is executed with precision and foresight. This includes meticulous planning, rigorous evaluation of potential solutions, and the implementation of robust security measures to safeguard against data breaches, all while adhering to budgetary limits and ensuring the new solutions complement the existing infrastructure.

    Solutions and Innovative Approaches to Stay Competitive

    To navigate the turbulent waters of IT procurement, embracing innovative solutions and approaches is crucial for maintaining competitiveness. This includes leveraging process efficiency through digital platforms and artificial intelligence, which can automate routine tasks, streamline procurement operations, and facilitate data-driven decision-making. Additionally, adopting flexible procurement models can provide the agility needed to adapt to changing technology landscapes, ensuring that organizations are not only meeting their current needs but are also poised for future growth and innovation.

    Enhancing Efficiency through Best Practices and Strong Supplier Relationships

    At the heart of enhancing procurement efficiency lies the strategic cultivation of strong supplier relationships and the adoption of best practices. By carefully evaluating TCO and considering options that align with organizational goals, procurement teams can make informed decisions that yield long-term benefits. Artificial intelligence can further refine these processes, enabling more precise evaluations and fostering partnerships with potential suppliers that are mutually beneficial. This strategic approach not only streamlines procurement operations but also ensures that investments are aligned with the organization’s broader strategic objectives.

    The Total Cost of Ownership (TCO) and Its Impact

    Understanding the Total Cost of Ownership (TCO) is pivotal in IT procurement, as it transcends the initial acquisition cost, encompassing all costs associated with the lifecycle of the asset. Evaluating TCO enables procurement teams to make more informed decisions, considering not just the purchase price but also operational, maintenance, and decommissioning costs. This holistic view ensures that the procured IT solutions are not only cost-effective but also align with the organization’s operational efficiency and long-term strategic goals. By prioritizing TCO, organizations can optimize their IT investments, ensuring maximum value and performance throughout the asset’s lifecycle.

    Future Trends and Innovations

    As we look to the future, the landscape of network infrastructure projects is set to be transformed by digital innovations. The continuous evolution of technology demands that organizations stay abreast of new trends and innovations, ensuring that their procurement strategies are not only responsive but also proactive in leveraging these advancements.

    Staying Ahead with Digital Procurement Platforms

    Staying Ahead with Digital Procurement Platfoms

    Digital procurement platforms are revolutionizing procurement processes, offering unprecedented levels of efficiency and transparency. These platforms enable organizations to streamline their procurement activities, from tendering to contract management, facilitating quicker decision-making and reducing administrative burdens. As procurement becomes increasingly digital, these platforms will play a pivotal role in transforming procurement operations, making them more agile and responsive to the dynamic needs of businesses.

    The Role of AI and Machine Learning in Enhancing Procurement Processes

    The integration of AI and machine learning into procurement processes heralds a new era of efficiency and innovation. These technologies can automate routine tasks, analyze vast amounts of data to identify trends and insights, and facilitate predictive analysis, enabling procurement teams to make more informed decisions. By enhancing process efficiency and providing deeper insights into supplier performance and market trends, AI and machine learning are set to redefine the procurement landscape, making it more strategic, efficient, and aligned with organizational goals.

    The Evolution of Network Infrastructure Procurement

    At the core of the evolution of network infrastructure procurement is the concept of lifecycle management. As technology rapidly advances, the need for a strategic approach to managing the entire lifecycle of network infrastructure—from planning and acquisition to maintenance and eventual decommissioning—becomes increasingly critical. This shift towards a more holistic view of procurement not only optimizes investments but also ensures that the infrastructure can adapt to future technological shifts, thereby supporting the long-term goals and resilience of organizations.

    Adapting to Global Team Needs at Scale

    In an era of globalization, adapting to the needs of global teams at scale has become a critical consideration in network infrastructure procurement. Organizations must ensure that their procurement strategies are flexible enough to support distributed teams across different geographies, cultures, and time zones. This requires a deep understanding of local market conditions, regulations, and technology standards, ensuring that the solutions procured are not only effective at a global scale but also customizable to meet local needs, thereby enhancing collaboration, efficiency, and productivity across the organization.

    Transforming Business Efficiency with End-to-End Procurement Services

    The integration of end-to-end procurement services has revolutionized the way organizations approach infrastructure development, from planning and design to supply and installation. This holistic approach has enabled businesses to leverage the full spectrum of procurement expertise, ensuring that each phase of the procurement process is executed with precision and aligned with the organization’s strategic objectives. The result is a seamless, efficient, and cost-effective procurement cycle that fosters innovation and agility.

    Success in the Words of our Clients: Small Business to Enterprise

    From the perspective of our diverse clientele, the impact of our procurement services is profound. Small businesses laud the tailored solutions that have allowed them to scale efficiently, while enterprises highlight the strategic value of having a partner that understands the complexities of their vast network. Across the board, clients appreciate the commitment to flexibility, expertise, and a client-centric approach, underscoring how these pillars have transformed their procurement practices and, by extension, their operational capabilities.

    Making the Right Choice for Your Organization

    Choosing the right procurement partner is pivotal in navigating the complexities of network infrastructure procurement. A forward-thinking partner offers not just immediate solutions but also anticipates future challenges, ensuring your procurement strategy is robust and adaptable. This strategic alignment is crucial in sustaining growth, driving innovation, and maintaining competitive edge in a rapidly changing technological landscape. Therefore, the decision should hinge on finding a partner that embodies flexibility, expertise, and a deep understanding of procurement best practices.

    Why Choose a Forward-Thinking Procurement Partner

    A forward-thinking procurement partner brings more than just expertise; they bring a vision that aligns with the evolving needs of your organization. They employ procurement best practices that not only address current requirements but also adapt to future changes, ensuring your procurement strategy remains effective and efficient. This adaptability is crucial for staying ahead in a competitive and technologically advanced marketplace, making the choice of such a partner an essential step towards achieving long-term success.

    We’ve been providing clients with assistance with their procurement for over 25 years and have relationships with all the major manufacturers.

    Flexibility, Expertise, and a Client-Centric Approach

    At the heart of a successful procurement strategy lies the trio of flexibility, expertise, and a client-centric approach. Flexibility ensures that your procurement processes can adapt to changing market dynamics and organizational needs. Expertise guarantees that the most current and effective procurement systems are in place, maximizing efficiency and value. A client-centric approach, meanwhile, ensures that solutions are tailored to meet the unique needs of your organization, from vendor reputation assessment to the successful supply and installation of network infrastructure.

    Final Thoughts on Network Infrastructure Procurement

    As we look towards the future of network infrastructure procurement, it’s clear that the landscape is undergoing profound change. The need to conduct market research to identify potential vendors, adapt to changing legislative requirements, and make strategic purchasing decisions has never been more critical. Organizations must embrace innovation in their procurement processes, leveraging advanced procurement systems and analytics to stay competitive. The journey of infrastructure procurement is complex, involving both consulting and non-consulting services, but with the right approach, it can drive significant value and contribute to the sustainable growth of your organization.

    The Road Ahead: Embracing Change and Innovation in IT Procurement

    Looking ahead to 2025, the trajectory for IT procurement is set towards greater integration of digital solutions, from inventory management systems that enhance business operations to technology procurement that aligns with organization’s requirements. The focus is on streamlining the procurement process, leveraging industry trends, and meeting both domestic and international legislative requirements and customer expectations. This shift not only promises to unlock the potential of procurement in driving business efficiency but also in reshaping how organizations approach equipment procurement, especially in the realm of networking equipment.

    Ready to Transform Your Network Infrastructure Procurement Strategy?

    As your organization contemplates the next steps in its procurement journey, the opportunity to transform your network infrastructure procurement strategy is within reach. Embracing change and innovation, guided by procurement focuses that prioritize adaptability, efficiency, and strategic vendor relationships, will be key. The future of procurement is not just about meeting immediate needs but unlocking the potential for growth, scalability, and sustainability. With the right partner and approach, your organization can navigate the complexities of today’s procurement landscape and emerge stronger, more agile, and ready for the challenges of tomorrow.

    Our page on network infrastructure procurement is here.

    Contact Us For More Information
  • Network Penetration Testing: An In-Depth Exploration

    Network Penetration Testing: An In-Depth Exploration

    Network Penetration Testing: An In-Depth Exploration

    Network penetration testing stands as a crucial practice for identifying vulnerabilities and security gaps within an organization’s network, aiming to fortify its defenses against cyber threats. By simulating attacks that a malicious actor might exploit, cybersecurity professionals can uncover critical insights into how to enhance network security measures.

    This comprehensive exploration delves into the methodologies employed by cybersecurity professionals to detect and address security gaps. The process not only prevents potential financial losses but also safeguards sensitive information from those seeking to gain unauthorized access, thereby maintaining the integrity and reputation of the organization.

    Understanding Network Penetration Testing

    At its core, network security testing is a methodical approach undertaken by cybersecurity professionals to identify and exploit security gaps, aiming to prevent malicious actors from gaining unauthorized access. This practice is pivotal in highlighting vulnerabilities and security flaws within a network’s architecture.

    Definition and Scope

    Network penetration testing, often referred to as network pen testing, is a security exercise designed to evaluate the resilience of a network’s defenses by simulating an attack from malicious entities. The scope of this testing encompasses various strategies and tools to identify weaknesses that could be exploited by attackers, offering critical insights for enhancing network security.

    The Network Penetration Testing Process

    Information Gathering

    The initial phase of network pen testing involves thorough information gathering about the target environment. This step is crucial for understanding the landscape of the network, including identifying devices, services, and applications that are part of the network’s infrastructure. Such information lays the groundwork for subsequent testing phases.

    Planning and Vulnerability Scanning

    Following the collection of detailed information, the next step is planning and conducting vulnerability scanning. This phase aims to identify potential weaknesses within the target environment’s security posture. It involves the use of automated tools to systematically scan for vulnerabilities that could be exploited by attackers.

    Automated vs. Manual Testing

    This type of security testing employs both automated tools and manual techniques to uncover potential security issues. Automated tools are efficient for scanning a wide range of vulnerabilities quickly, whereas manual testing allows for a deeper, more nuanced exploration of complex security weaknesses that automated tools might miss.

    Analysis and Reporting

    Once testing is completed, the next critical step is the analysis and reporting of findings. This involves documenting the discovered security gaps and presenting them in a format that is actionable for stakeholders. This phase ensures that identified vulnerabilities are understood and addressed appropriately.

    Remediation and Retesting

    Addressing the identified technical vulnerabilities is a pivotal step in the network pen testing process. Remediation efforts are undertaken to patch or mitigate these weaknesses, followed by retesting to ensure that the fixes are effective and that no new vulnerabilities have been introduced during the remediation process.

    Types of Penetration Tests

    Cybersecurity professionals employ various types of penetration tests, including application penetration testing and vulnerability management, as part of a comprehensive security testing program. These tests are tailored to meet the specific security needs of an organization.

    Black Box, White Box, and Gray Box Testing

    Network Penetration Test Types

    Different approaches such as black box, white box, and gray box pen tests offer varied levels of access and information to the testers. These methodologies help in identifying vulnerabilities from different perspectives, simulating various attack scenarios to provide a thorough assessment of network security.

    Internal vs. External Penetration Testing

    Network penetration testing can be categorized into external and internal tests. External network penetration testing focuses on identifying vulnerabilities that could be exploited from outside the network, whereas internal penetration testing assesses risks from within the organization. This comprehensive testing process ensures a holistic security evaluation.

    The Importance of Network Penetration Testing

    Network penetration testing plays a vital role in bolstering an organization’s security posture, identifying vulnerabilities before they can be exploited by attackers, and ensuring compliance with regulations like PCI DSS.

    Enhancing Security Posture

    Through the identification and remediation of vulnerabilities, network penetration testing significantly enhances an organization’s security posture, making it more resilient against cyber attacks.

    Regulatory Compliance and Protecting Sensitive Data

    Adhering to standards such as PCI DSS is essential for organizations handling sensitive data. Network penetration testing ensures compliance with these regulations, thereby protecting against data breaches and potential penalties.

    Identifying and Mitigating Security Vulnerabilities

    Vulnerability scanners play a crucial role in network penetration testing by pinpointing security gaps that cyber attackers could exploit. These tools enable cybersecurity professionals to identify and assess the severity of vulnerabilities, providing a roadmap for prioritization and remediation. By systematically identifying and mitigating these vulnerabilities, organizations can significantly reduce their attack surface, making it harder for attackers to exploit vulnerabilities and gain unauthorized access.

    Preventing Financial Loss and Maintaining Reputation

    Network penetration testing is instrumental in safeguarding an organization’s financial stability and reputation. By identifying and addressing security risks before they are exploited, companies can avoid the costly consequences of data breaches, including regulatory fines, litigation costs, and loss of customer trust. Regular penetration testing demonstrates a commitment to security, helping to maintain and enhance an organization’s reputation in the marketplace.

    The Benefits of Performing Network Penetration Testing

    Carrying out network penetration tests offers invaluable benefits by uncovering security risks, allowing cybersecurity professionals to fortify the network against potential attacks. This proactive approach is fundamental in building a resilient security posture.

    Improved Security Measures and Controls

    Frequent network penetration testing leads to the continuous improvement of security measures and controls. It enables organizations to adapt their defenses in response to evolving cybersecurity threats and tactics. Implementing the recommendations from penetration testing reports strengthens the security infrastructure, making it more difficult for attackers to succeed.

    Prevention of Data Breaches and Network Intrusions

    One of the most significant benefits of network penetration testing is the prevention of data breaches. By simulating cyber-attacks, organizations can identify and rectify security weaknesses before they can be exploited by malicious actors. This proactive measure effectively reduces the likelihood of network intrusions, safeguarding sensitive information from unauthorized access and ensuring data integrity and confidentiality.

    Insights into Security Weaknesses

    Network penetration testing offers deep insights into an organization’s security weaknesses, revealing vulnerabilities that might not be detected through conventional security audits. This process allows for the identification of multiple vulnerabilities across network devices, applications, and systems, providing a comprehensive view of potential security threats and enabling targeted improvements to the security framework.

    Enterprise Security Built for Small Business

    Network penetration testing is not just for large enterprises; it’s equally vital for small businesses. It offers a scalable solution to identify and mitigate potential security threats that could otherwise devastate a smaller organization. By tailoring the testing process to the specific needs and resources of a small business, cybersecurity measures can be effectively implemented, providing robust security without the need for enterprise-level resources.

    Steps in the Network Penetration Testing Cycle

    The network penetration testing cycle involves several key steps, from initial consultation to reporting and follow-up, ensuring a thorough examination and strengthening of the network’s security posture.

    Steps In The Network Penetration Testing Cycle

    Initial Consultation and Goal Setting

    The initial phase of network penetration tests involves consulting with the client to understand their network infrastructure, identify critical assets, and set specific goals. This stage is crucial for establishing the scope of the test, including the identification of security controls, phishing attacks, and potential security vulnerabilities. By aligning the testing process with the client’s expectations and industry security standards, a targeted approach can be developed to address identified vulnerabilities effectively.

    Understanding Client Expectations

    Understanding client expectations is fundamental in the initial consultation phase of network penetration testing. This dialogue helps define the scope, targets, and objectives of the test, ensuring that the process aligns with the client’s security concerns and requirements. It sets the stage for a customized testing strategy that focuses on the client’s most critical assets and potential security risks, aiming to strengthen their overall security posture.

    Reconnaissance and Discovery Phase

    The reconnaissance and discovery phase is a critical step in network penetration testing, where testers gather information about the target network. Through vulnerability assessments, testers identify exploitable weaknesses in the system’s defenses. This phase lays the groundwork for developing a strategic approach to the penetration test, focusing on areas where the network is most vulnerable to attack.

    Execution of Pen Tests

    The execution phase of penetration testing involves actively exploiting identified vulnerabilities to assess the network’s defenses. This crucial step determines the real-world effectiveness of existing security measures.

    Technical and Human Approaches

    Penetration testing combines technical and human approaches to evaluate network security comprehensively. Technical methods involve using software tools to automate the scanning and exploitation of vulnerabilities, while human approaches leverage social engineering tactics, such as phishing emails, to mimic the actions of cyber attackers. This blend of techniques ensures a thorough assessment of both the network’s technical defenses and the organization’s readiness against social engineering threats.

    Reporting, Recommendations, and Follow-Up

    Following the execution of penetration tests, the findings are compiled into a detailed report, offering actionable recommendations for improving network security. This stage is critical for closing security gaps and enhancing the network’s defense mechanisms.

    Sample Network Pen Test Report

    A sample network penetration test report typically includes an executive summary, methodology, findings, and recommendations. It details the vulnerabilities discovered, such as SQL injections, brute force attacks, and the effectiveness of phishing emails. The report also assesses the risk level of each finding and proposes remedial actions to prevent unauthorized access to the target, providing a roadmap for strengthening the network’s security posture.

    Free Penetration Testing Policy Template

    Offering a free penetration testing policy template empowers organizations to establish a foundational framework addressing technical vulnerabilities within their network. This template serves as a starting point, guiding businesses through the essential elements of a comprehensive penetration testing policy. It ensures that all aspects of the testing process are covered, fostering a secure and resilient network environment.

    Letter of Attestation (LOA) and Certification

    Upon the successful completion of a penetration test, a Letter of Attestation (LOA) and certification are provided. These documents serve as a testament to the organization’s commitment to security, verifying that the network has been rigorously tested against known vulnerabilities. They instill confidence among stakeholders and customers, assuring them that the network’s integrity meets high security standards.

    Common Network Security Threats Addressed

    In the realm of network security, penetration testing plays a critical role in safeguarding against threats such as malware, phishing, DDoS attacks, and more. By simulating real-world attacks, experts can identify and rectify vulnerabilities, thereby protecting sensitive data from unauthorized access. This proactive approach is indispensable in an era where cyber threats are continuously evolving.

    Malware and Phishing Attacks

    Malware and phishing attacks are prevalent threats that seek to exploit network vulnerabilities to steal sensitive information. Penetration testing helps in identifying potential security gaps that could be leveraged by attackers to deploy malware or execute phishing campaigns. By addressing these vulnerabilities, organizations can significantly reduce the risk of such attacks.

    DDoS Attacks and Advanced Persistent Threats (APTs)

    DDoS attacks and Advanced Persistent Threats (APTs) represent sophisticated challenges to network security. These attacks aim to disrupt services or stealthily infiltrate networks over extended periods. Penetration testing enables organizations to detect and mitigate the risk of these threats, thereby safeguarding the continuity and integrity of business operations.

    Drive-by Downloads and DNS Attacks

    Drive-by downloads and DNS attacks are insidious methods attackers use to compromise networks. Through penetration testing, vulnerabilities that could be exploited by these attacks are identified and remediated. This preemptive action helps in preventing unauthorized access and the potential manipulation of DNS entries, thus maintaining the network’s security posture.

    Tools and Technologies for Network Penetration Testing

    The landscape of network penetration testing is enriched with a variety of tools and technologies designed to identify and exploit vulnerabilities. These tools, ranging from automated scanners to sophisticated testing software, enable security professionals to simulate attacks under controlled conditions. Their usage is crucial for uncovering weaknesses before they can be exploited by malicious actors.

    Automated Tools and Software

    Automated tools and software play a pivotal role in the efficiency and effectiveness of network penetration testing. These solutions expedite the process of detecting vulnerabilities, allowing for a more comprehensive assessment in a shorter timeframe. Automation also aids in the repetitive and meticulous tasks required in penetration testing, ensuring no stone is left unturned.

    Integrations and Use Cases

    The integration of penetration testing tools into the broader security ecosystem enhances the overall effectiveness of security strategies. These tools can be tailored to specific use cases, providing targeted insights into vulnerabilities and potential attack vectors. Such integrations facilitate a holistic approach to security, encompassing both prevention and proactive detection.

    Resources for AppSec Risk Management

    Resources dedicated to Application Security (AppSec) risk management are invaluable for organizations aiming to fortify their networks against threats. These resources, including guidelines, best practices, and tools for detecting vulnerabilities, play a critical role in developing a robust security framework. They enable businesses to address the evolving landscape of cyber threats with confidence.

    FAQs on Network Penetration Testing

    Network penetration testing is a crucial practice for identifying and addressing security vulnerabilities within network and systems. It involves a comprehensive testing process that simulates real-world attacks on target systems to uncover weaknesses.

    Why is Pen Testing Critical?

    Penetration testing, or pen testing, is critical because it helps organizations identify and fix security issues before attackers can exploit them. This proactive approach is essential for protecting sensitive data, ensuring business continuity, and maintaining customer trust. Through pen testing, companies can better understand their security posture and make informed decisions to strengthen their defenses.

    The Difference Between Pen Testing and Vulnerability Scanning

    While both penetration testing and vulnerability scanning are essential for network security, there are key differences. Penetration testing involves a deliberate and in-depth exploration intended to exploit vulnerabilities and assess the actual risk to the system. In contrast, vulnerability scanning is an automated process that identifies potential vulnerabilities. Penetration testing offers a more nuanced understanding of security flaws, incorporating both external and internal perspectives, including external network penetration testing and internal penetration testing.

    How Often Should Pen Tests Be Conducted?

    The frequency of penetration testing depends on various factors, including the organization’s size, complexity of the network, and sensitivity of the data handled. Generally, it’s recommended to conduct pen tests annually or whenever significant changes are made to the network infrastructure. This ensures that new vulnerabilities are promptly identified and addressed, keeping the network secure.

    Choosing the Right Pen Testing Service

    Selecting the right penetration testing service is vital for achieving meaningful security outcomes. Organizations should look for providers with a proven track record, comprehensive testing methodologies, and the ability to offer actionable insights. It’s also important to choose a service that aligns with the organization’s specific needs, whether focusing on external network penetration testing, internal penetration testing, or both.

    Navigating Challenges and Best Practices

    Network penetration testing is fraught with challenges that require a fine balance between technical know-how and ethical practice. Best practices in this field not only demand a deep understanding of the latest vulnerabilities and threats but also necessitate a commitment to continuous learning and adaptation. As the digital landscape evolves, so too must the strategies and methodologies of penetration testers to ensure they provide the most comprehensive and effective security assessments possible.

    Ethical Considerations and Legal Implications

    When conducting testing activities, it’s crucial to navigate the thin line between ethical hacking and potential legal breaches. Testers must have explicit permission from the organization owning the network before commencing any tests. This not only prevents legal repercussions but also ensures that all testing activities are conducted with integrity and respect for privacy and data protection laws. Ethical considerations form the backbone of trustworthy penetration testing, safeguarding both the tester and the client from unintended consequences.

    Balancing Automated and Manual Testing Methods

    In the realm of network penetration testing, striking the right balance between automated tools and manual testing methods is key to identifying potential weaknesses effectively. Automated tools can scan vast networks quickly, flagging issues for further investigation. However, they may not catch every nuance of a complex security system. Manual testing, on the other hand, allows for a more detailed and nuanced understanding of a network’s vulnerabilities, though it requires significant time and expertise. The best approach combines both, leveraging the speed of automation with the depth of manual analysis.

    Ensuring Comprehensive Coverage and Depth of Testing

    Achieving comprehensive coverage and depth in testing is crucial for a thorough security assessment. This involves not only a wide-ranging examination across the network to identify vulnerabilities but also a deep dive into how these vulnerabilities could be exploited. It’s about understanding not just the breadth of potential security gaps but also the depth of the risk they pose. This level of thoroughness ensures that even the most hidden vulnerabilities are uncovered and addressed.

    Continuous Improvement in Pen Testing Methodologies

    The landscape of cybersecurity is ever-changing, and so the methodologies used in penetration testing must evolve accordingly. Continuous improvement is essential, with testers updating their strategies to incorporate the latest findings from vulnerability scans and adapting to new types of cyber threats. This iterative process not only enhances the effectiveness of penetration tests but also ensures that defenses are always a step ahead of potential attackers.

    Future Trends in Network Penetration Testing

    As digital threats become more sophisticated, the field of network penetration testing is rapidly evolving. Future trends point towards an increased reliance on artificial intelligence and machine learning to automate and refine testing processes. Additionally, the integration of new technologies promises to enhance the capabilities of testers, allowing for more dynamic and effective security assessments. Staying ahead of these trends is crucial for organizations looking to protect their networks from the ever-growing threat landscape.

    The Evolution of Cyber Threats and Pen Testing Techniques

    The cyber threat landscape is in a constant state of flux, with attackers continuously developing new methods to exploit network vulnerabilities. In response, penetration testing techniques are also evolving, employing more sophisticated tools and approaches to identify and mitigate these threats effectively. This ongoing arms race between attackers and defenders highlights the importance of adaptive, innovative testing strategies to safeguard digital assets.

    The Role of AI and Machine Learning in Pen Testing

    Artificial intelligence and machine learning are playing an increasingly pivotal role in network penetration testing. These technologies offer the potential to automate complex tasks, allowing for more efficient identification of vulnerabilities and prediction of potential attack vectors. By harnessing the power of AI and machine learning, testers can analyze vast amounts of data more accurately and swiftly, leading to more effective and timely security measures.

    Enhancing Pen Testing with Emerging Technologies

    The integration of emerging technologies into network penetration testing is set to revolutionize the field. From blockchain to quantum computing, these new tools offer unique advantages in enhancing security assessments. They provide innovative ways to test network defenses, ensuring that organizations can stay one step ahead of cybercriminals. The future of penetration testing lies in the ability to adapt and incorporate these cutting-edge technologies, offering unprecedented levels of network security.

    The Critical Role of Network Penetration Testing in Today’s Digital World

    In the digital age, where cyber threats evolve with alarming speed, network penetration testing emerges as a cornerstone of a robust cybersecurity strategy. By simulating real-world attacks, ethical hackers utilize a comprehensive array of tools and techniques, including port scanning and testing for vulnerabilities like buffer overflow, to uncover network vulnerabilities. This proactive approach enables security teams to identify and remediate security vulnerabilities before malicious actors can exploit them, safeguarding sensitive data against both external threats and internal threats. Moreover, penetration testing goes beyond mere risk assessments; it provides actionable insights into enhancing security measures, refining security policies, and fortifying application security across various platforms, including mobile applications. As businesses continue to navigate the complex cyber landscape, the role of penetration testing in maintaining a resilient defense against both known and emerging threats cannot be overstated. It embodies a critical layer of defense, ensuring that security checks, risk management, and mitigation strategies are always aligned with the organization’s evolving security needs.

    Our Network Penetration information is here.

    Contact Us For More Information
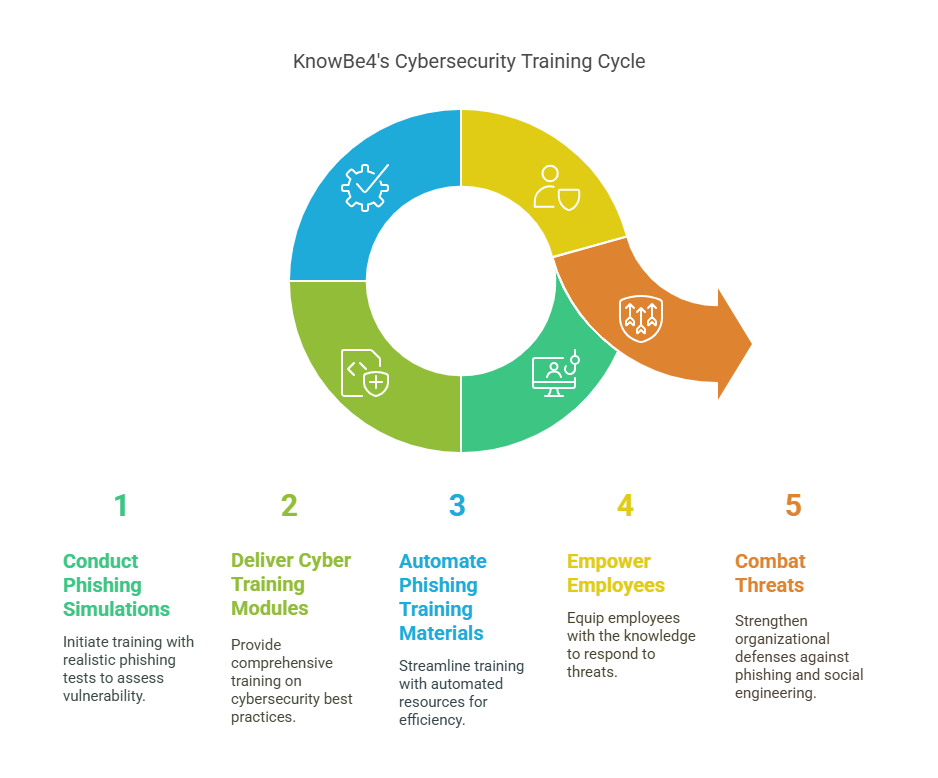
  • Optrics Engineering Makes the 2018 Branham 300

    Optrics Engineering Makes the 2018 Branham 300

    Optrics is excited to announce making #212 on the prestigious Branham 300 Listing of Top 250 Canadian ICT Companies for 2018.

    Company representatives cite increased opportunities in wireless networking solutionsvirtualization solutionsnetwork attached storage, and anti-spam solutions as strong contributors to their success in the past year, as well as disaster recovery, and penetration testing/training.

    About the Branham 300

    The Branham 300, now in its 24th year, is the best-known and most widely referenced listing of Canada’s top public and private ICT companies, ranked by revenue. The list also tracks the top ICT multinationals operating in Canada plus Up and Comers, those young Canadian companies Branham thinks will be big hits soon.

    Canada’s Top 250 ICT companies delivered another banner year in 2018, generating a revenue total of $105.3 billion, an increase of 9.6% compared to the year prior. So we have a new revenue record for Canada’s Top 250 technology companies, and a growth rate almost double the previous year.

    Quote

    “The 2018 edition of the Branham300 once again shows revenue growth in Canada’s ICT industry. Revenue generated by the Top 250 tech companies in Canada has grown every year since 2009…”
    Wayne Gudbranson, CEO, Branham Group

    About Optrics

    A pioneer in online marketing and commerce, Optrics Engineering provides clients with expertise in computer networking, network storage, security, and IT infrastructure management.

    Among the many internationally known organizations that have relied on Optrics for technology solutions are NASA, Microsoft, Best Buy, US Army, Air Force and Navy, DND, Boeing, Lockheed Martin and Mercedes-Benz.

    Locally, the firm has worked with the University of Alberta, AMA, Capital Health, Fountain Tire and Fraser, Milner & Casgrain. For a larger client listing go to: www.Optrics.com/clients.

    For more information, contact:
    Blair Zingle, CEO or Scott Young, COO
    Optrics Engineering
    780.430.6240
    Email: info@Optrics.com

  • Optrics Engineering Makes the 2017 Branham 300

    Optrics Engineering Makes the 2017 Branham 300

    Optrics is excited to announce making #234 on the prestigious Branham 300 Listing of Top 250 Canadian ICT Companies for 2017.

    Company representatives cite increased opportunities in wireless networking solutions, virtualization solutionsnetwork attached storage, and anti-spam solutions as strong contributors to their success in the past year, as well as disaster recovery, and penetration testing/training.

    About the Branham 300

    The Branham 300, now in its 24th year, is the best-known and most widely referenced listing of Canada’s top public and private ICT companies, ranked by revenue. The list also tracks the top ICT multinationals operating in Canada plus Up and Comers, those young Canadian companies Branham thinks will be big hits soon.

    Canada’s Top 250 ICT companies delivered another banner year in 2015, generating a revenue total of $105.3 billion, an increase of 9.6% compared to the year prior. So we have a new revenue record for Canada’s Top 250 technology companies, and a growth rate almost double the previous year.

    Quote

    “The Branham 300 is designed to promote Canada’s Information and Communication Technology industry and the people who build technology businesses in Canada. This year, we were thrilled to see Canada’s Top 250 companies set another revenue record. It is a testament to the strength of our ICT sector.”
    Wayne Gudbranson, CEO, Branham Group

    About Optrics

    A pioneer in online marketing and commerce, Optrics Engineering provides clients with expertise in computer networking, network storage, security, and IT infrastructure management.

    Among the many internationally known organizations that have relied on Optrics for technology solutions are NASA, Microsoft, Best Buy, US Army, Air Force and Navy, DND, Boeing, Lockheed Martin and Mercedes-Benz.

    Locally, the firm has worked with the University of Alberta, AMA, Alberta Health Services, Capital Health, Fountain Tire and Fraser, Milner & Casgrain.

    For more information, contact:
    Blair Zingle, CEO or Scott Young, COO
    Optrics Engineering
    780.430.6240
    Email: info@Optrics.com

  • Optrics Engineering Makes the 2016 Branham 300

    Optrics Engineering Makes the 2016 Branham 300

    Optrics is excited to announce making #227 on the prestigious Branham 300 Listing of Top Canadian ICT Companies for 2016.

    Company representatives cite increased opportunities in wireless networking solutionsvirtualization solutionsnetwork attached storage, and anti-spam solutions as strong contributors to their success in the past year.

    About the Branham 300

    The Branham 300, now in its 23rd year, is the best-known and most widely referenced listing of Canada’s top public and private ICT companies, ranked by revenue. The list also tracks the top ICT multinationals operating in Canada plus Up and Comers, those young Canadian companies Branham thinks will be big hits soon.

    Canada’s Top 250 ICT companies delivered another banner year in 2015, generating a revenue total of $96.1 billion, an increase of 5.7% compared to the year prior. That new record number was driven by the impressive performance of Canada’s Top 250 tech companies: 75% of the Top 250 generated revenue growth, and 54% delivered double- and even triple-digit increases.

    Quote

    “The Branham 300 is designed to promote Canada’s Information and Communication Technology industry and the people who build technology businesses in Canada. This year, we were thrilled to see Canada’s Top 250 companies set another revenue record. It is a testament to the strength of our ICT sector.”
    Wayne Gudbranson, CEO, Branham Group

    About Optrics

    A pioneer in online marketing and commerce, Optrics Engineering provides clients with expertise in computer networking, network storage, security, and IT infrastructure management.

    Among the many internationally known organizations that have relied on Optrics for technology solutions are NASA, Microsoft, Best Buy, US Army, Air Force and Navy, DND, Boeing, Lockheed Martin and Mercedes-Benz.

    Locally, the firm has worked with the University of Alberta, AMA, Capital Health, Fountain Tire and Fraser, Milner & Casgrain. For a larger client listing go to: www.Optrics.com/clients.

    For more information, contact:
    Blair Zingle, CEO or Scott Young, COO
    Optrics Engineering
    780.430.6240
    Email: info@Optrics.com