Author: Optrics

  • The $2.9B Healthcare Hack That Could Have Been Prevented With One Simple Security Step

    The $2.9B Healthcare Hack That Could Have Been Prevented With One Simple Security Step

    Healthcare’s $2.9B Wake-Up Call: Lessons from the Change Healthcare Breach 🏥

    The recent cyberattack on Change Healthcare serves as a stark reminder of the devastating impact a single security breach can have on healthcare operations. When BlackCat ransomware group successfully infiltrated Change Healthcare’s systems, they didn’t just compromise one organization – they disrupted the entire healthcare payment infrastructure across the United States.

    The Perfect Storm: Why Healthcare is a Prime Target 🎯

    Healthcare organizations face unique cybersecurity challenges that make them particularly vulnerable to attacks. The combination of valuable patient data, complex IT infrastructure, and the critical nature of healthcare services creates an attractive target for cybercriminals. In the case of Change Healthcare, these factors converged with devastating results:

    • Compromised credentials through a Citrix portal
    • Absence of proper multi-factor authentication
    • Lateral movement across interconnected systems
    • Theft of sensitive patient data and medical records

    Beyond the Breach: Understanding the True Cost 💰

    The financial impact of the Change Healthcare attack is staggering – an estimated $2.9 billion in recovery costs, legal fees, and settlements. But the real cost extends far beyond dollars and cents. Healthcare providers nationwide experienced disruptions in claims processing, payment systems, and patient care delivery.

    Protecting Healthcare Data with ManageEngine DataSecurity Plus

    ManageEngine DataSecurity Plus offers healthcare organizations a comprehensive solution to prevent similar breaches. Key capabilities include:

    • Real-time file activity monitoring
    • Data discovery and classification
    • Access management and control
    • Threat detection and response
    • Compliance reporting and documentation

    The platform specifically addresses the top five security threats to healthcare data, helping organizations maintain both security and compliance with healthcare regulations.

    Building a Resilient Healthcare Security Strategy

    ManageEngine’s approach emphasizes the importance of a multi-layered security strategy that protects data in all states – at rest, in use, and in motion. This comprehensive protection is crucial for healthcare organizations handling sensitive patient information and complex payment systems.

    🚨 Critical Takeaway: The Change Healthcare breach demonstrates that basic security measures like MFA could have prevented a multi-billion dollar disaster. Is your organization prepared to prevent a similar attack?

    Ready to strengthen your healthcare organization’s security posture? Schedule a demo of ManageEngine DataSecurity Plus today and take the first step toward robust data protection.
    Contact Us Now

  • Why Your Dark Web Alerts Matter: A Security Pro’s Guide to Actionable Defense

    Why Your Dark Web Alerts Matter: A Security Pro’s Guide to Actionable Defense

    Dark Web Monitoring: From Alert Fatigue to Actionable Intelligence

    In today’s digital landscape, the dark web serves as a bustling marketplace for stolen corporate data, yet many organizations remain unaware of their exposure until it’s too late. While security teams are bombarded with alerts daily, dark web notifications shouldn’t be dismissed as just another security warning—they’re often the first indication that your organization’s defenses have been compromised. 🚨

    Understanding the Hidden Threat Landscape

    The scale of dark web operations is staggering, with billions of stolen credentials circulating at any given moment. What’s more concerning is the time gap between data theft and discovery: sensitive information often trades hands multiple times before organizations realize they’ve been compromised.

    Moving Beyond Passive Security

    Traditional security approaches that wait for breach notifications or rely solely on perimeter defenses are no longer sufficient. The key to modern cybersecurity lies in proactive monitoring and rapid response—transforming dark web alerts from noise into actionable intelligence.

    Building an Effective Response Strategy

    ManageEngine’s integrated security solutions offer a comprehensive approach to addressing dark web threats:

    1. Immediate Password Protection
    • ManageEngine Password Manager Pro enables rapid password changes when credentials are compromised
    • Streamlines implementation of multi-factor authentication
    • Ensures unique, strong passwords across all systems
    1. Vulnerability Management
    • ManageEngine Vulnerability Manager Plus helps identify and patch security gaps
    • Provides structured vulnerability assessment and remediation
    • Reduces the attack surface that could lead to future breaches
    1. Advanced Analytics
    • ManageEngine Analytics Plus transforms security data into actionable insights
    • Enables pattern recognition for proactive threat prevention
    • Helps security teams identify and address recurring vulnerabilities

    Turning Insights into Action

    Each dark web alert presents an opportunity to strengthen your security posture. By leveraging ManageEngine’s suite of solutions, organizations can:

    • Quickly identify and contain potential breaches
    • Implement stronger access controls
    • Build a more resilient security framework
    • Transform reactive security into proactive defense

    Ready to transform your approach to dark web threats? Book a demo today to see how ManageEngine’s security solutions can help protect your organization from emerging threats. 🔒

    Contact Us Now

  • New FBI Alert: How Middle Eastern Students Are Being Targeted by Elite Social Engineers

    New FBI Alert: How Middle Eastern Students Are Being Targeted by Elite Social Engineers

    🚨 FBI Warns of Sophisticated Phishing Scam Targeting International Students

    In a concerning development for educational institutions and international students alike, the FBI has identified a sophisticated phishing campaign specifically targeting Middle Eastern students in the United States. This elaborate scheme demonstrates how cybercriminals are evolving their tactics to exploit vulnerable populations through carefully researched, culturally-aware social engineering attacks.

    The Anatomy of a Targeted Attack

    The scammers behind this campaign have developed a multi-channel approach that shows an unprecedented level of preparation and cultural awareness. By impersonating officials from various agencies – including the Department of Homeland Security (DHS), Homeland Security Investigations (HSI), and even embassies from students’ home countries – these attackers create a convincing facade of authority.

    What makes these attacks particularly effective is their use of:

    • Phone number spoofing of legitimate government agencies
    • Native language speakers matching the purported origin
    • Detailed knowledge of visa processes and documentation
    • High-pressure tactics leveraging immigration concerns

    Why This Matters for Security Teams

    This campaign represents a significant evolution in social engineering tactics. Rather than casting a wide net with generic phishing emails, cybercriminals are now conducting detailed research on specific demographic groups, understanding their unique vulnerabilities, and crafting highly targeted approaches.

    For security professionals, this raises several critical considerations:

    • Traditional email-based security measures alone are insufficient
    • Staff need training on multi-channel social engineering tactics
    • Cultural awareness must be incorporated into security protocols

    Building Effective Defenses

    KnowBe4 Security Awareness Training platform helps organizations prepare for these sophisticated attacks by providing comprehensive training that goes beyond basic phishing awareness. Their program includes:

    • Simulated authority-based social engineering scenarios
    • Multi-language training materials
    • Cultural awareness components
    • Continuous assessment and reinforcement

    Protecting Your Organization

    The FBI recommends several immediate steps to verify legitimate communications:

    1. Never provide personal information over phone or email
    2. Hang up and contact agencies through officially verified channels
    3. Report suspicious contacts to relevant authorities

    The KnowBe4 platform builds on these recommendations by creating a security-aware culture that empowers users to recognize and respond appropriately to social engineering attempts, regardless of the channel or technique used.

    🤔 Is your organization prepared to protect vulnerable populations from sophisticated social engineering attacks? Book a demo with KnowBe4 today to learn how security awareness training can strengthen your human firewall.

    Book Your KnowBe4 Demo Now

  • The Human Firewall: Why Your 2024 Ransomware Strategy Must Go Beyond Technology

    The Human Firewall: Why Your 2024 Ransomware Strategy Must Go Beyond Technology

    Ransomware in 2024: Why the Threat Isn’t Going Away 🚨

    Despite what you might have heard, ransomware remains a persistent and evolving threat in today’s cybersecurity landscape. While recent data from Marsh’s 2024 UK cyber insurance claims report shows a 20% year-over-year decrease in ransomware incidents, the numbers still significantly exceed pre-pandemic levels – serving as a stark reminder that cybercriminals continue to adapt and evolve their tactics.

    The Changing Face of Ransomware Attacks

    Today’s ransomware threats are more sophisticated and targeted than ever before. Cybercriminals aren’t just encrypting data anymore; they’re escalating to more aggressive tactics, including threats of physical violence and public data leaks. This evolution requires organizations to maintain constant vigilance and adapt their security strategies accordingly.

    The Human Factor: Your Greatest Vulnerability (and Asset) 🔑

    While technical controls are crucial, social engineering remains the primary vector for initiating breaches. Cybercriminals excel at exploiting human psychology, using emotions like trust, curiosity, and fear to gain unauthorized access to systems. This is where KnowBe4 Security Awareness Training becomes invaluable, helping organizations:

    • Build a security-conscious workforce
    • Stay current with evolving threat landscapes
    • Create a strong security culture across all departments
    • Reduce vulnerability to social engineering attacks

    Building a Comprehensive Defense Strategy 🛡️

    A robust cybersecurity approach must combine:

    1. Regular security awareness training
    2. Secure backup systems
    3. Advanced threat detection
    4. Comprehensive incident response plans
    5. Ongoing risk assessments

    KnowBe4’s platform addresses the critical human element of this equation, providing organizations with the tools and training needed to transform employees from potential vulnerabilities into active defenders against cyber threats.

    The Path Forward

    Organizations can no longer view ransomware as someone else’s problem. The threat landscape continues to evolve, and while fewer organizations are paying ransoms thanks to improved security measures, the sophistication of attacks continues to increase.

    🤔 Ask yourself: Is your organization treating security awareness training as a one-time event or an ongoing process? In today’s threat landscape, continuous education and vigilance are no longer optional – they’re essential for survival.

    Ready to strengthen your organization’s human firewall? [Contact us today to learn more about implementing KnowBe4’s Security Awareness Training program.]

    Book Your KnowBe4 Demo Now

  • DragonForce Alert: The Ransomware Game-Changer That’s Outsmarting Traditional Security

    DragonForce Alert: The Ransomware Game-Changer That’s Outsmarting Traditional Security

    The Rise of DragonForce: How Ransomware Evolution Demands Smarter Defense

    The ransomware landscape is experiencing a seismic shift as DragonForce emerges as a disruptive force in the cybercrime ecosystem. This relatively new player isn’t just targeting businesses—it’s actively working to reshape the entire ransomware-as-a-service (RaaS) market through aggressive tactics and innovative attack methods.

    A New Brand of Cyber Threat 🚨

    DragonForce’s approach marks a departure from traditional ransomware operations. Beyond targeting conventional IT infrastructure, the group has expanded into virtualized environments like VMware ESXi, demonstrating unprecedented versatility. Their March 2025 introduction of a flexible affiliate model—allowing partners to utilize DragonForce’s tools under their own brands—signals a concerning evolution in ransomware sophistication.

    The Human Element: Social Engineering Takes Center Stage

    What makes DragonForce and its affiliates particularly dangerous is their masterful blend of social engineering and technical exploitation. Their attacks often begin with something as simple as a conversation with IT help desk staff, proving that human interaction, not technical vulnerabilities, is frequently the initial point of compromise.

    The group’s use of sophisticated infostealers like Vidar and Raccoon to harvest credentials and session tokens enables increasingly convincing impersonation attacks, often bypassing traditional security measures—including multi-factor authentication.

    Defending Against the New Wave

    Sophos research reveals that organizations need a comprehensive defense strategy that goes beyond traditional security measures. Key recommendations include:

    • Implementing robust browser isolation
    • Deploying enterprise-grade password managers
    • Utilizing advanced endpoint detection specifically targeted at infostealers
    • Maintaining continuous identity monitoring
    • Establishing strict IT support channel verification protocols
    • Conducting regular social engineering simulation exercises

    The Sophos Advantage

    Sophos’s integrated security ecosystem provides the multi-layered protection needed to combat these evolving threats. Through the Sophos Counter Threat Unit’s continuous monitoring and analysis, organizations gain access to real-time threat intelligence and adaptive defense capabilities that help stay ahead of groups like DragonForce.

    Looking Ahead 🔮

    The emergence of more aggressive and sophisticated ransomware operators like DragonForce signals a new era in cybersecurity challenges. Organizations must recognize that effective defense requires both cutting-edge technical solutions and enhanced human vigilance.

    Ready to strengthen your organization’s defense against evolving ransomware threats? Contact us today to learn how Sophos can help protect your business with industry-leading security solutions and expert threat intelligence.

    #Cybersecurity #Ransomware #ThreatIntelligence #SocialEngineering #Sophos

    Contact Us Now

  • What Is Penetration Testing? Discover vPenTest’s Automated Edge for Cybersecurity (2025 Guide)

    What Is Penetration Testing? Discover vPenTest’s Automated Edge for Cybersecurity (2025 Guide)

    328fddb4 3c33 4650 b307 ce8341c91ab7

    Introduction to Penetration Testing

    Definition and Purpose

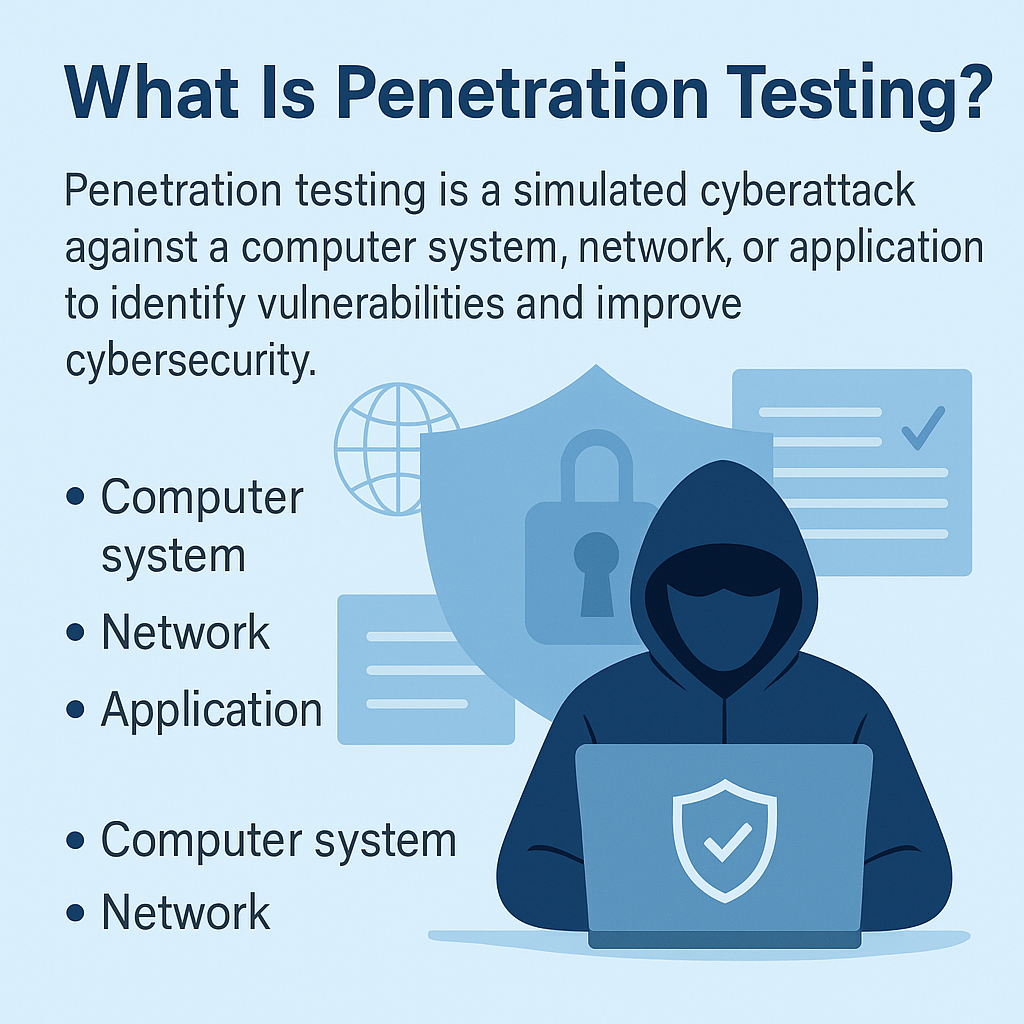
    Penetration testing, or pen testing, is the process of simulating cyberattacks on a system, network, or application to identify security weaknesses. It plays a vital role in proactive cybersecurity and helps organizations understand how a real-world hacker could exploit their vulnerabilities.

    As threats evolve, traditional pen testing methods struggle to keep up. That’s where vPenTest by Vonahi Security, a Kaseya-owned company, steps in—offering automated, scalable, and affordable pen testing that’s reshaping the landscape.

    Offered by Optrics Engineering, a trusted Kaseya partner, vPenTest empowers IT teams to test their environments anytime, at any frequency – without the wait.

    How Penetration Testing Works with vPenTest

    Types of Pen Tests

    • Black Box: Simulates outsider attacks
    • White Box: Provides deep internal analysis
    • Gray Box: Mixes both for targeted testing

    Automated vs Manual Testing

    Traditional Pen TestvPenTest by Vonahi
    High scheduling wait timesOn-demand testing, anytime
    Manual process, human errorFully automated, error-resistant
    Costly and inconsistentAffordable, consistent, repeatable

    vPenTest automates the same methods used by expert testers and executes simulated attacks – such as malware deployment, privilege escalation, and data exfiltration – at scale.

    Benefits of Using vPenTest

    Scalable & Frequent Testing

    No limits. Monthly? Weekly? Even daily? You choose the cadence.

    Immediate, Actionable Insights

    • Real-time vulnerability alerts
    • Trend tracking over time
    • Executive and technical reports in 48 hours

    Cost-Effective Protection

    Compared to traditional pen tests, vPenTest delivers up to 50% savings without sacrificing depth or accuracy.

    Core Phases of vPenTest’s Methodology

    1. Pre-Engagement: Define scope, goals, permissions
    2. Information Gathering: Reconnaissance and enumeration
    3. Exploitation: Simulates real-world attack paths
    4. Post-Exploitation: Tests persistence and lateral movement
    5. Reporting: Delivered fast, easy to understand
    6. Remediation: Helps you fix vulnerabilities efficiently

    Who Should Use vPenTest?

    Organizations of All Sizes

    vPenTest is used by small IT teams and large enterprises alike – affordable for all.

    Regulated Industries

    Perfect for businesses bound by compliance such as:

    • PCI-DSS
    • HIPAA
    • GDPR
    • NIST frameworks

    Why Optrics Engineering Recommends vPenTest

    As a certified Kaseya partner, Optrics Engineering helps clients streamline security operations and testing with zero friction.

    • Automate recurring pen tests
    • Close compliance gaps fast
    • Backed by Kaseya and Vonahi Security

    Ready to see it in action? Request a Demo Now

    FAQs About vPenTest

    Is automated penetration testing accurate?

    Yes. It’s built by certified ethical hackers using real-world tactics.

    What’s the turnaround for reports?

    Both executive and technical reports are delivered within 48 hours.

    Can vPenTest integrate with our SIEM?

    Yes, full logging and data export support are included.

    What attack types are covered?

    • Malware simulation
    • Password and brute-force attacks
    • Privilege escalation
    • Data exfiltration tests

    What’s deployment like?

    Simple. Install the agent, define the scope, and start testing – no delays.

    Conclusion

    Penetration testing is no longer optional. With vPenTest, you gain year-round security insights at a fraction of the cost of traditional testing.

    Optrics Engineering is here to help you take control of your cybersecurity, proactively.

    🚀 Get Started Now: Schedule a Demo and discover how easy modern security can be.

    Free vPenTest Demo

  • AI-Powered Social Engineering: Why Your Security Training Is Already Obsolete

    AI-Powered Social Engineering: Why Your Security Training Is Already Obsolete

    The Rising Tide of AI-Powered Social Engineering: Why Traditional Security Awareness Isn’t Enough 🔒

    In today’s rapidly evolving threat landscape, cybercriminals are leveraging artificial intelligence to launch increasingly sophisticated social engineering attacks. With a staggering 1,265% increase in AI-generated phishing attacks since 2022, organizations face an unprecedented challenge in protecting their digital assets and human resources.

    The New Face of Social Engineering 🎯

    Modern social engineering attacks have evolved far beyond simple email phishing. Threat actors, like the notorious Scattered Spider group, now orchestrate multi-channel campaigns that simultaneously leverage SMS, email, phone calls, and collaboration tools. Perhaps most concerning is their targeting of help desk and outsourced IT functions – traditionally considered trusted channels within organizations.

    The statistics are sobering: before implementing proper security awareness training, one in three employees (33.1%) will click on phishing links. Even more alarming is that the median time between a user opening a phishing email and clicking a malicious link is just 21 seconds.

    Beyond Traditional Security Awareness

    Traditional security awareness training no longer suffices in this AI-powered threat environment. Organizations need a comprehensive human risk management approach that can:

    • Monitor and respond to threats across multiple communication channels
    • Address sophisticated MFA manipulation tactics
    • Provide continuous assessment and targeted training
    • Transform employees from security vulnerabilities into active defenders

    The KnowBe4 Advantage

    The KnowBe4 Security Awareness Training platform takes a multi-faceted approach to these challenges. Their solution employs multiple specialized AI agents working in concert to address various aspects of human risk management. This sophisticated approach has delivered impressive results: organizations using KnowBe4 report an 83% reduction in their Phish-prone Percentage within 12 months.

    The platform’s effectiveness translates directly to the bottom line, with customers seeing cybersecurity insurance premium reductions of up to 20% and ROI between 362% and 650% in the first year.

    Transform Your Security Posture

    The threat landscape will continue to evolve, but one thing remains clear: human risk management must be at the foundation of any effective cybersecurity strategy.

    Ready to transform your employees from security vulnerabilities into your strongest defense? Book a demo with KnowBe4 today and discover how their AI-powered platform can revolutionize your organization’s security awareness posture. 🚀

    Book Your KnowBe4 Demo Now

  • Email Attacks Drive 60% of Cyber Insurance Claims: Is Your Human Firewall Ready?

    Email Attacks Drive 60% of Cyber Insurance Claims: Is Your Human Firewall Ready?

    The Rising Tide of Email-Based Cyber Insurance Claims: What Security Leaders Need to Know 🚨

    Email-based cyberattacks continue to dominate the threat landscape, with recent data showing that business email compromise (BEC) attacks and funds transfer fraud now account for a staggering 60% of cyber insurance claims. More concerning still, the average loss from these incidents has climbed to $35,000 – a 23% increase that signals growing sophistication in attack methods.

    Understanding the Impact

    The financial implications of email-based attacks extend far beyond immediate losses. Organizations face mounting costs related to:

    • Legal expenses and compliance requirements
    • Incident response and forensics
    • Data mining and analysis
    • Customer notifications and reputation management

    Regional variations tell an interesting story, with U.S. claims averaging $36,000, while both Canadian and UK claims hover around $22,000. This disparity highlights the global nature of the threat and the need for region-specific defense strategies.

    Industry-Specific Vulnerabilities

    Not all sectors face equal risk. Organizations handling sensitive data – whether financial records, healthcare information, or intellectual property – face heightened targeting from cybercriminals. Meanwhile, industries with lower security awareness often fall victim to opportunistic attacks like phishing and credential theft.

    Building a Human-Centric Defense 🛡️

    As attack methods grow more sophisticated, organizations are recognizing that technology alone cannot prevent successful breaches. This is where KnowBe4 Security Awareness Training proves invaluable, offering:

    • Comprehensive phishing simulation programs
    • Industry-specific training approaches
    • Compliance-ready documentation
    • Cultural transformation tools

    KnowBe4 platform has already strengthened security postures across more than 70,000 organizations worldwide, creating an essential defense layer specifically designed to combat social engineering attacks.

    Take Action Today

    With email-based attacks showing no signs of slowing, the question isn’t if your organization will be targeted, but when. Are your employees prepared to be your strongest line of defense?

    Book a demo with our team to learn how KnowBe4’s Security Awareness Training can help protect your organization from costly email-based attacks and strengthen your overall security posture.

    Book Your KnowBe4 Demo Now

  • Beyond Cisco Prime: Why Network Teams Are Choosing ManageEngine for Their 2025 Migration

    Beyond Cisco Prime: Why Network Teams Are Choosing ManageEngine for Their 2025 Migration

    Navigating the Cisco Prime Infrastructure End-of-Life: A Strategic Guide for Network Teams 🔄

    As September 2025 approaches, organizations running Cisco Prime Infrastructure face a critical transition period. With end-of-support looming, IT teams must act now to ensure continuous network management capabilities and maintain robust security postures. Let’s explore the challenges and opportunities this change presents.

    Understanding the Impact 🚨

    The end-of-life announcement for Cisco Prime Infrastructure creates several immediate concerns for network administrators:

    • Potential security vulnerabilities from unsupported systems
    • Compliance risks in regulated industries
    • Operational disruptions if migration is delayed
    • Resource allocation challenges during transition

    Why Cisco DNA Center May Not Be the Answer

    While Cisco positions DNA Center as the natural successor, many organizations are discovering limitations that make this transition less than ideal:

    • High licensing costs and complex pricing structures
    • Limited multi-vendor support in heterogeneous environments
    • Steep learning curve and deployment complexity
    • Required specialized expertise for maintenance

    ManageEngine Network Configuration Manager: A Forward-Looking Alternative

    ManageEngine Network Configuration Manager emerges as a comprehensive solution that addresses these challenges while offering additional advantages:

    Advanced Automation & Control

    • Programmable configlets for streamlined management
    • Real-time change tracking and centralized backups
    • Automated compliance checks and remediation
    • Integrated firmware vulnerability scanning

    Enterprise-Ready Features

    • Multi-vendor support out of the box
    • User-friendly interface requiring minimal training
    • Transparent pricing model
    • Rapid deployment capabilities

    Future-Proof Compliance

    The upcoming Q3 2025 release will introduce visual flow-based compliance management, offering:

    • Context-aware compliance monitoring
    • Dynamic policy enforcement
    • Automated remediation workflows
    • Real-time security posture assessment

    Making the Transition

    Organizations can significantly reduce migration risks by:

    1. Conducting infrastructure assessments early
    2. Developing a phased transition plan
    3. Leveraging ManageEngine’s migration tools and support
    4. Training teams on new capabilities proactively

    The Time to Act Is Now

    With less than two years until Cisco Prime Infrastructure‘s end-of-support date, organizations need to begin their transition strategy immediately. ManageEngine Network Configuration Manager offers a clear path forward, combining advanced capabilities with practical usability and transparent costs.

    🔒 Ready to secure your network’s future? Schedule a personalized demo of ManageEngine Network Configuration Manager today and discover how to make your transition seamless and successful.