Tag: Vonahi

  • Stop Pretending Your Security Works: Why Pen Testing Changes Everything in 2024

    Stop Pretending Your Security Works: Why Pen Testing Changes Everything in 2024

    Why Penetration Testing Should Be Your #1 Security Priority in 2024

    In today’s rapidly evolving threat landscape, organizations face a critical challenge: the growing gap between perceived and actual security. While many businesses invest heavily in security tools and proudly display their compliance certificates, these measures alone aren’t enough to guarantee protection against sophisticated cyber attacks. 🛡️

    Beyond Checkbox Security

    Traditional security approaches often create a false sense of safety. Automated vulnerability scanners and compliance audits, while valuable, can miss complex attack vectors that today’s adversaries routinely exploit. It’s like having a home security system that only checks if the doors are locked – without testing if the locks actually work.

    Real-world attacks don’t follow a checklist, and neither should your security validation strategy. This is where penetration testing emerges as the most critical security control for modern organizations.

    The Power of Adversary Simulation

    Vonahi’s approach to penetration testing goes beyond conventional methods by combining human expertise with advanced automation. Their platform simulates real-world attack scenarios, uncovering vulnerabilities that automated tools might miss:

    • Complex attack chains that exploit multiple weaknesses
    • Human error factors in security processes
    • Misconfigurations in seemingly compliant systems
    • Business logic flaws that only human testers can identify

    Continuous Validation for Modern Security

    The days of annual penetration tests are over. Modern infrastructure changes constantly, and so do cyber threats. Vonahi’s innovative platform enables organizations to implement continuous security validation without the traditional bottlenecks and high costs of manual testing.

    This continuous approach delivers several key benefits:

    • Faster identification of security gaps
    • More cost-effective testing processes
    • Regular validation of security controls
    • Actionable data for security improvements
    • Clear reporting for stakeholders and boards

    Moving Beyond “Paper Security”

    For IT and security teams, Vonahi’s platform transforms penetration testing from a periodic checkbox exercise into a powerful, ongoing security validation tool. This shift not only strengthens your security posture but also provides tangible evidence of security effectiveness to customers, regulators, and insurers.

    🔒 Ready to move beyond traditional security measures and implement truly effective security validation? Book a demo with Vonahi today and discover how continuous penetration testing can transform your security strategy.
    Free vPenTest Demo

  • Why Security Leaders Are Ditching Manual Penetration Testing for Good

    Why Security Leaders Are Ditching Manual Penetration Testing for Good

    Automating Security Compliance: Beyond the Checkbox Approach

    In today’s rapidly evolving threat landscape, organizations can no longer afford to view security compliance as an annual checkbox exercise. The growing sophistication of cyber attacks demands a more dynamic, continuous approach to security assessment and validation.

    The Compliance-Security Gap

    While achieving compliance with frameworks like PCI DSS, HIPAA, SOC 2, and ISO 27001 is crucial, simply meeting these requirements doesn’t guarantee protection against real-world threats. This disconnect between compliance and actual security posture leaves many organizations vulnerable, even when they’ve technically “passed” their audits.

    Bridging the Gap with Automated Penetration Testing

    Vonahi vPenTest platform represents a significant shift in how organizations approach both compliance and security validation. By automating the penetration testing process, vPenTest enables organizations to:

    • Conduct regular, on-demand security assessments without the traditional costs and coordination challenges
    • Generate standardized, compliance-ready reports that streamline audit preparation
    • Validate security controls against realistic attack scenarios
    • Monitor and improve security posture continuously, rather than periodically

    Beyond Traditional Penetration Testing

    The traditional approach to penetration testing – hiring external vendors for annual assessments – is both costly and increasingly insufficient for modern security needs. Vonahi’s automated platform democratizes access to advanced security testing, making it accessible to organizations of all sizes through a self-service portal and subscription model.

    Strategic Benefits for Security Leaders

    With vPenTest, security and IT teams can:

    • Demonstrate real security outcomes to stakeholders
    • Track progress and improvements over time
    • Reduce time spent managing vendors and coordinating assessments
    • Optimize security testing budgets through automation

    Creating a Culture of Continuous Security

    Perhaps most importantly, Vonahi’s approach helps foster a proactive security culture. Regular, automated assessments become part of the organizational rhythm, rather than a dreaded annual event. This continuous validation provides security leaders with ongoing confidence in their defensive measures and helps maintain a strong security posture between compliance audits.

    Ready to Transform Your Security Testing?

    Don’t wait for your next audit to discover security gaps. Experience how Vonahi’s automated penetration testing platform can help your organization move beyond checkbox compliance to achieve real security resilience.

    [Book a Demo] to see vPenTest in action and learn how automated security validation can strengthen your compliance program while protecting against real-world threats.


    Free vPenTest Demo

  • Maximize Your Security ROI: Why Grey Box Testing Is The Missing Layer In Your Defense Strategy

    Maximize Your Security ROI: Why Grey Box Testing Is The Missing Layer In Your Defense Strategy

    Why Grey Box Penetration Testing Is Your Security Program’s Missing Link

    In today’s evolving threat landscape, organizations need more than just basic security testing to stay ahead of sophisticated attackers. While black box and white box penetration testing have their place, there’s a powerful middle ground that many security programs overlook: grey box penetration testing. 🔍

    The Reality of Modern Attacks

    Here’s an uncomfortable truth: most successful cyber attacks aren’t completely blind. Threat actors often possess some level of insider knowledge, whether through social engineering, initial compromise, or public information gathering. This reality makes grey box penetration testing particularly relevant, as it mirrors real-world attack scenarios by providing testers with partial system knowledge.

    Beyond Traditional Testing Limitations

    Traditional testing approaches often fall short in critical ways:

    • Black box testing can miss configuration vulnerabilities
    • White box testing is resource-intensive and time-consuming
    • Neither fully simulates common attack patterns involving partial system knowledge

    The Strategic Advantage of Grey Box Testing

    Vonahi’s grey box penetration testing solution offers a strategic sweet spot, delivering several key benefits:

    • More efficient discovery of configuration errors and access control weaknesses
    • Better simulation of realistic attack scenarios
    • Balanced resource utilization compared to other testing methods
    • Enhanced ability to identify lateral movement risks
    • Stronger support for compliance requirements

    Why It Matters for Your Organization

    The rise in sophisticated cyber attacks makes grey box testing increasingly crucial. Vonahi’s approach helps organizations uncover vulnerabilities that might be missed by other testing methodologies, particularly those involving internal misconfigurations or complex attack chains.

    Security teams using Vonahi’s grey box testing can:

    • Identify and address security blind spots
    • Optimize security investments through focused testing
    • Build stakeholder confidence with comprehensive security validation
    • Adapt more quickly to emerging threats
    • Support compliance initiatives with detailed insights

    Future-Proofing Your Security Testing

    As cyber threats continue to evolve, static testing approaches no longer suffice. Grey box testing represents a more dynamic, adaptive security validation strategy that keeps pace with modern attack techniques.

    🚨 Did you know? According to recent industry research, attacks involving some level of insider knowledge have increased by over 47% in the past year, making grey box testing more relevant than ever.

    Ready to enhance your security testing strategy? Book a demo with our team to see how Vonahi’s grey box penetration testing can strengthen your organization’s security posture.


    Contact Us Now

  • Mastering Modern Security: The 8 Critical Penetration Tests Your Organization Can’t Ignore

    Mastering Modern Security: The 8 Critical Penetration Tests Your Organization Can’t Ignore

    Understanding the 8 Types of Penetration Testing: A Comprehensive Guide

    In today's evolving threat landscape, understanding your organization's security vulnerabilities isn't just good practice—it's essential for survival. 🔒 While many organizations conduct regular security assessments, penetration testing stands out as a crucial proactive measure that can make the difference between security confidence and costly breaches.

    The Eight Pillars of Modern Penetration Testing

    Vonahi's comprehensive approach to penetration testing encompasses eight distinct types, each addressing specific areas of potential vulnerability:

    1. External Network Testing
    2. Internal Network Testing
    3. Wireless Network Testing
    4. Web Application Testing
    5. Social Engineering Assessments
    6. Physical Security Testing
    7. Cloud Infrastructure Testing
    8. Red Team Engagements

    Each of these testing methodologies serves a unique purpose in your security arsenal. For instance, while external network testing helps identify vulnerabilities that could be exploited from outside your organization, internal testing focuses on threats that could emerge from within your network perimeter.

    Why Different Types Matter

    🎯 The diversity of modern cyber attacks requires a multi-faceted defense strategy. Vonahi's specialized approach ensures that organizations can:

    • Identify vulnerabilities that automated scanning tools might miss
    • Meet specific compliance requirements for frameworks like PCI DSS, HIPAA, and SOC 2
    • Demonstrate security due diligence to stakeholders and partners
    • Adapt security strategies to evolving threat landscapes

    Beyond Traditional Testing

    What sets Vonahi's penetration testing apart is its comprehensive coverage across different attack surfaces. Their approach doesn't just check boxes—it simulates real-world attack scenarios that modern organizations face daily. From testing cloud infrastructure misconfigurations to assessing employee susceptibility to social engineering, Vonahi's methodology provides actionable intelligence for improving security posture.

    The Strategic Advantage

    Regular penetration testing isn't just about finding vulnerabilities—it's about maintaining a robust security position in an increasingly complex digital landscape. By partnering with Vonahi, organizations can:

    • Proactively identify and remediate security gaps
    • Strengthen stakeholder trust
    • Support compliance initiatives
    • Stay ahead of evolving threats

    Making Security a Continuous Journey

    🚨 Security isn't a destination—it's a journey. Regular penetration testing with Vonahi helps organizations maintain a strong security posture while adapting to new threats and challenges. As cyber attacks become more sophisticated, having a comprehensive testing strategy becomes increasingly critical.

    Ready to strengthen your organization's security posture? Book a consultation with our team to learn how Vonahi's penetration testing services can help protect your critical assets and maintain stakeholder trust.

    Free vPenTest Demo

  • Why Smart MSPs Are Ditching Manual Pen Testing for Automation

    Why Smart MSPs Are Ditching Manual Pen Testing for Automation

    The Rise of Automated Penetration Testing: A Game-Changer for MSPs

    In today’s rapidly evolving threat landscape, Managed Service Providers (MSPs) face mounting pressure to deliver robust security services while maintaining efficiency and profitability. As high-profile breaches continue making headlines, the need for comprehensive penetration testing has never been greater – but traditional manual approaches often fall short of modern demands. 🔒

    Why Traditional Pen Testing No Longer Cuts It

    Manual penetration testing, while valuable, comes with significant limitations: high costs, slow execution, and difficulty scaling across multiple clients. In an era where cyber threats evolve daily, periodic testing simply isn’t enough to ensure continuous security coverage.

    Enter Automated Penetration Testing

    This is where automated solutions like Vonahi vPenTests are transforming the industry. By leveraging automation, MSPs can now offer continuous, comprehensive security assessments that were previously impossible with manual methods alone.

    Key Benefits of Automated Pen Testing:

    • 24/7 execution and continuous updates
    • Rapid scanning of complex environments
    • Consistent, repeatable results
    • Standardized methodology across clients
    • Prioritized remediation insights
    • Streamlined compliance reporting

    The Business Case for MSPs

    Vonahi’s automated penetration testing solution addresses several critical challenges facing MSPs today:

    1. Resource Optimization: Reduce reliance on scarce security talent while maintaining high-quality assessments
    2. Scalability: Efficiently manage security testing across growing client bases
    3. Compliance Support: Streamline audit documentation and regulatory requirements
    4. Competitive Advantage: Stand out in the market with modern, continuous offensive security capabilities

    Real Impact on Security Operations

    By implementing automated penetration testing, MSPs can detect and address vulnerabilities before attackers exploit them. The platform’s ability to emulate actual attack techniques while providing actionable remediation guidance helps organizations stay ahead of emerging threats.

    Making the Transition

    For MSPs looking to enhance their security offerings, Vonahi’s vPenTest represents a strategic opportunity to modernize penetration testing services. The solution combines comprehensive testing capabilities with the efficiency and scalability that modern MSPs require.

    🚀 Ready to transform your penetration testing capabilities? Book a demo today to see how Vonahi can help your MSP deliver more value while improving operational efficiency.


    Free vPenTest Demo

  • Automated Pen Testing: The $250,000 Security Gap You Can’t Afford to Ignore

    Automated Pen Testing: The $250,000 Security Gap You Can’t Afford to Ignore

    The True Cost of Cyber Attacks: Why Regular Penetration Testing is No Longer Optional

    In today’s digital landscape, cybersecurity isn’t just about protecting data—it’s about protecting your bottom line. Recent findings from the Kaseya Security Survey Report 2023 reveal a stark reality: over half of organizations faced losses exceeding $50,000 from a single cyber incident, with 21% reporting damages of more than $250,000. 🚨

    Beyond Traditional Security Measures

    While many organizations rely on routine vulnerability assessments, these static evaluations fall short in today’s dynamic threat landscape. The key difference? Penetration testing actively simulates real-world cyber attacks, providing actionable insights into exploitable weaknesses that matter most to your security posture.

    Why Traditional Approaches Fall Short

    • Infrequent testing leaves gaps in security awareness
    • Static assessments miss evolving threat patterns
    • Annual compliance-driven testing isn’t enough to stay protected
    • Resource constraints limit comprehensive security validation

    The Game-Changing Role of Automated Penetration Testing

    Vonahi’s innovative approach to automated penetration testing is transforming how organizations approach security validation. By leveraging automation, businesses can now conduct regular, thorough penetration tests without the traditional barriers of cost and resource constraints.

    Key Benefits of Automated Pen Testing:

    1. Continuous Security Validation – Monthly testing becomes feasible and affordable
    2. Real-World Attack Simulation – Understand genuine security gaps, not just theoretical vulnerabilities
    3. Efficient Resource Allocation – Prioritize remediation based on actual risk levels
    4. Streamlined Compliance – Maintain regulatory requirements while enhancing actual security

    The MSP Opportunity

    For Managed Service Providers, Vonahi automated penetration testing platform opens new revenue streams while delivering enhanced value to clients. By offering regular penetration testing as a service, MSPs can help clients stay ahead of emerging threats while building recurring revenue.

    Making the Shift to Proactive Security

    The message is clear: organizations need to be “attack-ready, not just audit-ready.” With automated solutions from Vonahi, regular penetration testing becomes an accessible, strategic necessity rather than an occasional checkbox exercise.

    🔒 Ready to transform your security validation approach? Book a demo today to see how Vonahi’s automated penetration testing can protect your organization from costly cyber incidents while streamlining your security operations.

    #cybersecurity #pentesting #infosec #automation #MSP


    Free vPenTest Demo

  • What Is Penetration Testing? Discover vPenTest’s Automated Edge for Cybersecurity (2025 Guide)

    What Is Penetration Testing? Discover vPenTest’s Automated Edge for Cybersecurity (2025 Guide)

    328fddb4 3c33 4650 b307 ce8341c91ab7

    Introduction to Penetration Testing

    Definition and Purpose

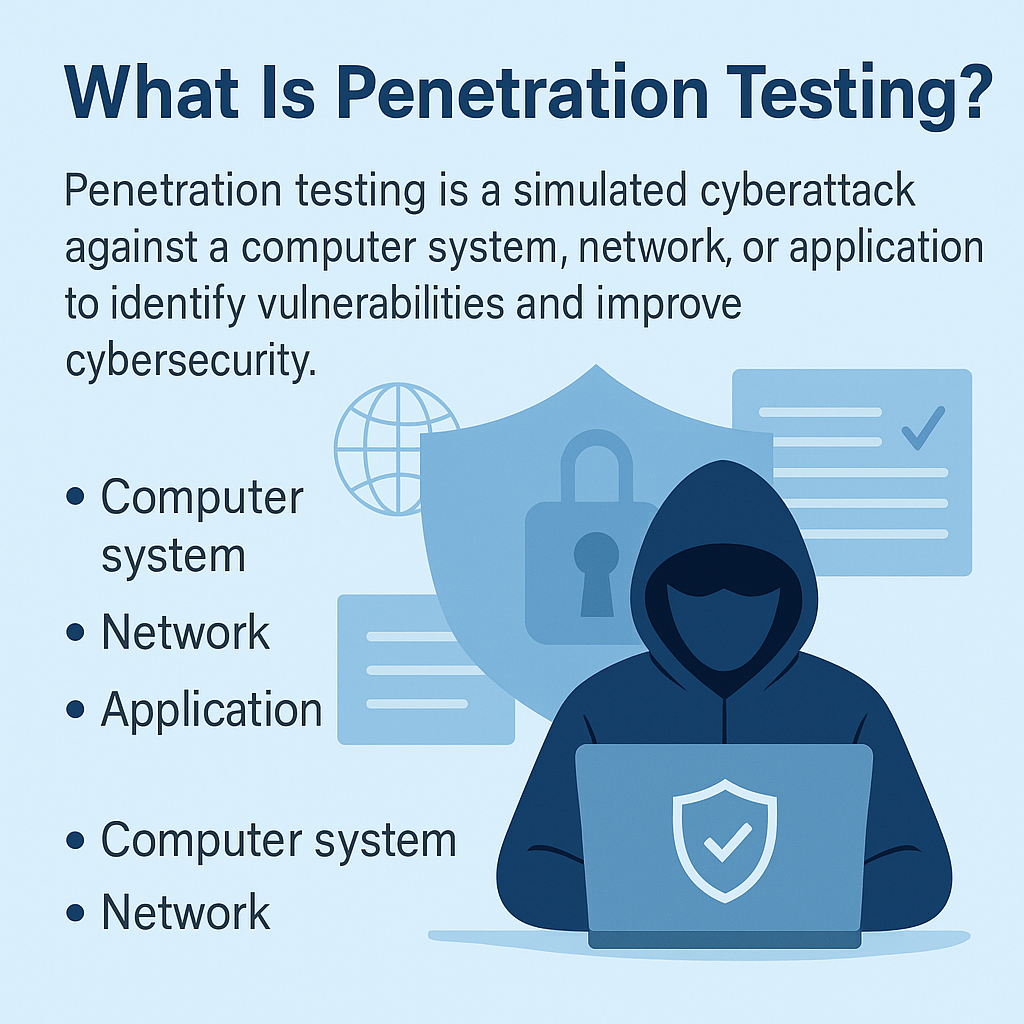
    Penetration testing, or pen testing, is the process of simulating cyberattacks on a system, network, or application to identify security weaknesses. It plays a vital role in proactive cybersecurity and helps organizations understand how a real-world hacker could exploit their vulnerabilities.

    As threats evolve, traditional pen testing methods struggle to keep up. That’s where vPenTest by Vonahi Security, a Kaseya-owned company, steps in—offering automated, scalable, and affordable pen testing that’s reshaping the landscape.

    Offered by Optrics Engineering, a trusted Kaseya partner, vPenTest empowers IT teams to test their environments anytime, at any frequency – without the wait.

    How Penetration Testing Works with vPenTest

    Types of Pen Tests

    • Black Box: Simulates outsider attacks
    • White Box: Provides deep internal analysis
    • Gray Box: Mixes both for targeted testing

    Automated vs Manual Testing

    Traditional Pen TestvPenTest by Vonahi
    High scheduling wait timesOn-demand testing, anytime
    Manual process, human errorFully automated, error-resistant
    Costly and inconsistentAffordable, consistent, repeatable

    vPenTest automates the same methods used by expert testers and executes simulated attacks – such as malware deployment, privilege escalation, and data exfiltration – at scale.

    Benefits of Using vPenTest

    Scalable & Frequent Testing

    No limits. Monthly? Weekly? Even daily? You choose the cadence.

    Immediate, Actionable Insights

    • Real-time vulnerability alerts
    • Trend tracking over time
    • Executive and technical reports in 48 hours

    Cost-Effective Protection

    Compared to traditional pen tests, vPenTest delivers up to 50% savings without sacrificing depth or accuracy.

    Core Phases of vPenTest’s Methodology

    1. Pre-Engagement: Define scope, goals, permissions
    2. Information Gathering: Reconnaissance and enumeration
    3. Exploitation: Simulates real-world attack paths
    4. Post-Exploitation: Tests persistence and lateral movement
    5. Reporting: Delivered fast, easy to understand
    6. Remediation: Helps you fix vulnerabilities efficiently

    Who Should Use vPenTest?

    Organizations of All Sizes

    vPenTest is used by small IT teams and large enterprises alike – affordable for all.

    Regulated Industries

    Perfect for businesses bound by compliance such as:

    • PCI-DSS
    • HIPAA
    • GDPR
    • NIST frameworks

    Why Optrics Engineering Recommends vPenTest

    As a certified Kaseya partner, Optrics Engineering helps clients streamline security operations and testing with zero friction.

    • Automate recurring pen tests
    • Close compliance gaps fast
    • Backed by Kaseya and Vonahi Security

    Ready to see it in action? Request a Demo Now

    FAQs About vPenTest

    Is automated penetration testing accurate?

    Yes. It’s built by certified ethical hackers using real-world tactics.

    What’s the turnaround for reports?

    Both executive and technical reports are delivered within 48 hours.

    Can vPenTest integrate with our SIEM?

    Yes, full logging and data export support are included.

    What attack types are covered?

    • Malware simulation
    • Password and brute-force attacks
    • Privilege escalation
    • Data exfiltration tests

    What’s deployment like?

    Simple. Install the agent, define the scope, and start testing – no delays.

    Conclusion

    Penetration testing is no longer optional. With vPenTest, you gain year-round security insights at a fraction of the cost of traditional testing.

    Optrics Engineering is here to help you take control of your cybersecurity, proactively.

    🚀 Get Started Now: Schedule a Demo and discover how easy modern security can be.

    Free vPenTest Demo