Category: Email Security

  • Scattered Spider’s Secret Weapon: Why Your IT Help Desk is Now Your Biggest Security Risk

    Scattered Spider’s Secret Weapon: Why Your IT Help Desk is Now Your Biggest Security Risk

    Scattered Spider: How Social Engineering Tactics Are Bypassing Enterprise Security

    In an era where technical security controls are stronger than ever, cybercriminal groups are turning to an age-old tactic with a modern twist: social engineering. The Scattered Spider group has emerged as a particularly sophisticated threat actor, targeting large enterprises through their help desk and IT support channels. 🎯

    The Human Element: A New Vector of Attack

    Recent investigations reveal a disturbing trend: Scattered Spider operators are masterfully exploiting human vulnerabilities rather than technical weaknesses. Their tactics include impersonating both employees seeking help and IT staff offering support, particularly targeting organizations with outsourced IT functions or large help desk operations.

    What makes these attacks particularly concerning is their exploitation of legitimate business tools and processes:

    • Weaponizing collaboration platforms like Microsoft Teams
    • Launching MFA fatigue attacks through repeated push notifications
    • Directly soliciting one-time passcodes through social manipulation
    • Exploiting the distributed nature of modern IT support systems

    Why Traditional Security Measures Aren’t Enough

    The success of these attacks highlights a critical gap in many organization’s security strategies. While robust technical controls like MFA are essential, they’re no longer sufficient on their own. Scattered Spider has demonstrated that even the strongest authentication methods can be bypassed when users aren’t properly trained to recognize and respond to social engineering attempts.

    Building Human-Centric Security with KnowBe4

    This is where the KnowBe4 Security Awareness Training platform becomes crucial. By providing comprehensive training that addresses modern social engineering tactics, organizations can:

    • Educate staff about sophisticated phishing and impersonation attempts
    • Build resilience against MFA bypass techniques
    • Establish clear procedures for validating IT support contacts
    • Create a security-aware culture that serves as a human firewall

    The platform specifically addresses emerging threats like collaboration tool exploitation and helps organizations develop robust verification protocols for support requests.

    A Call to Action

    As Scattered Spider and similar groups continue to evolve their tactics, the question isn’t if your organization will be targeted, but when. Are your employees prepared to recognize and respond to these sophisticated social engineering attempts?

    🔒 Take the first step in strengthening your human security layer. Contact us today to learn how KnowBe4’s Security Awareness Training can help protect your organization against these evolving threats.
    Book Your KnowBe4 Demo Now

  • 49 Seconds to Hack: Why Your Email Security Can’t Keep Up with Modern Phishing

    49 Seconds to Hack: Why Your Email Security Can’t Keep Up with Modern Phishing

    The 49-Second Security Crisis: Why Modern Phishing Attacks Leave No Room for Error

    In the ever-evolving landscape of cybersecurity threats, a disturbing new trend has emerged: the lightning-fast execution of phishing attacks. Recent research reveals that the window between a user opening a malicious email and having their credentials compromised has shrunk to just 49 seconds. This unprecedented speed presents a critical challenge for security teams worldwide. 🚨

    The Race Against Time

    The statistics are sobering. When an employee receives a phishing email, they typically click on malicious links within 21 seconds. If credential entry is involved, the entire compromise process takes less than a minute. With phishing email volume up 17.3% and a 47% increase in attacks bypassing secure email gateways, organizations face a perfect storm of rapid-fire threats.

    AI: A Double-Edged Sword

    Making matters worse, artificial intelligence has become a game-changer in the phishing landscape. KnowBe4’s Threat Research team has discovered that over 82.6% of phishing emails now leverage AI technology, enabling attackers to craft increasingly persuasive messages that can fool even sophisticated email security systems.

    Building Human Resilience

    While the threat landscape may seem daunting, there’s hope. KnowBe4 Security Awareness Training has proven remarkably effective at reducing phishing vulnerability across organizations of all sizes. The data tells a compelling story:

    • Anti-Phishing Before training: 33.1% of employees likely to fall for phishing attempts
    • After 90 days: 40% reduction in susceptibility
    • After one year: 86% reduction, dropping to just 4.1% vulnerability
    • After three years: Further improvement to 3.6% vulnerability rate

    Industry-Specific Impact

    The effectiveness of security awareness training varies by sector, with healthcare organizations starting at a 41.9% vulnerability rate compared to government entities at 28.2%. However, consistent training through KnowBe4’s platform has achieved 90-93% improvement rates even in the most vulnerable industries.

    🎯 The Bottom Line

    In a world where phishing attacks execute in less time than it takes to read this sentence, traditional reactive security measures simply can’t keep up. The solution lies in preparing employees to recognize and respond to threats instantly through comprehensive security awareness training.

    Ready to strengthen your organization’s human firewall? Contact us today to learn how KnowBe4’s Security Awareness Training can transform your security posture and protect your business from lightning-fast phishing attacks.

    Book Your KnowBe4 Demo Now

  • AI-Powered Phishing Attacks Surge 1,265%: Why Your Human Firewall Matters More Than Ever

    AI-Powered Phishing Attacks Surge 1,265%: Why Your Human Firewall Matters More Than Ever

    The Perfect Storm: AI, Phishing, and the New Frontiers of Cybersecurity

    In the first quarter of 2025, we’re witnessing an unprecedented convergence of cyber threats that’s reshaping the security landscape. Phishing attacks have skyrocketed to become the primary attack vector in 50% of all cyber incidents—a staggering jump from just 10% in the previous quarter. But that’s just the beginning of what security professionals are up against. 🚨

    The Triple Threat: AI, Social Engineering, and Automated Attacks

    Today’s threat actors are wielding a powerful new arsenal. Generative AI is supercharging phishing campaigns, enabling convincing deepfake audio and sophisticated business email compromise (BEC) attacks at scale. The numbers are sobering: AI-powered phishing attacks have surged by an astronomical 1,265% since 2022, with 92% of polymorphic attacks now leveraging artificial intelligence.

    What’s more concerning is that traditional security measures are showing their limitations. Even robust solutions like Multi-Factor Authentication (MFA) are being bypassed by modern phishing kits using reverse-proxy methods. The democratization of cyber threats through Phishing-as-a-Service platforms means that sophisticated attacks are no longer limited to skilled adversaries.

    Building Organizational Resilience

    In this evolving threat landscape, technical controls alone aren’t enough. Organizations need a comprehensive approach that transforms every employee into an active participant in their security strategy. This is where KnowBe4 Security Awareness Training makes a critical difference.

    KnowBe4’s platform addresses modern threats through:

    • AI-driven automation and threat detection
    • Real-time phishing simulation and training
    • Community intelligence from 13+ million users globally
    • Rapid threat removal capabilities
    • Integrated human intelligence that turns users into security assets

    The Power of Human-Centric Security

    The KnowBe4 PhishER Plus platform takes security awareness to the next level by:

    • Reducing manual response workloads by up to 99%
    • Systematically removing threats from user inboxes
    • Converting real threats into actionable training opportunities
    • Building a proactive, educated workforce

    Looking Ahead

    As we navigate this new era of AI-enhanced threats, the key to organizational security lies in empowering every employee with the knowledge and tools to recognize and respond to sophisticated attacks. Security awareness isn’t just about training—it’s about creating a culture of security consciousness that serves as a competitive advantage.

    🔒 Ready to transform your security posture and build a human firewall against modern threats? Book a demo with KnowBe4 today and discover how security awareness training can become your strongest defense against evolving cyber threats.

    Book Your KnowBe4 Demo Now

  • MFA is Not Enough: How Modern Phishing Kits Are Outsmarting Your Security

    MFA is Not Enough: How Modern Phishing Kits Are Outsmarting Your Security

    The Rise of MFA-Bypass Phishing: Why Human Security Awareness Matters More Than Ever

    🚨 Just when you thought Multi-Factor Authentication (MFA) had your organization’s security locked down, cybercriminals have found new ways to bypass these essential controls. Modern phishing kits, armed with sophisticated reverse proxy capabilities, are making even MFA-protected accounts vulnerable to attack.

    The landscape of phishing attacks has evolved dramatically. Tools like Tycoon 2FA and Evilproxy now enable attackers to create nearly perfect replicas of legitimate websites, intercepting both credentials and authentication cookies. These sites are so convincing that even security-conscious users might miss the subtle differences in their browser’s address bar.

    The Democratization of Cybercrime

    Perhaps more concerning is the rise of Phishing-as-a-Service (PhaaS) platforms. These ready-made toolkits have lowered the barrier to entry for cybercrime, allowing virtually anyone to launch sophisticated phishing campaigns. This democratization of attack capabilities means organizations of all sizes face an elevated baseline threat.

    “The commoditization of phishing attacks through PhaaS platforms has created a perfect storm,” says Roger Grimes, Data-Driven Defense Evangelist at KnowBe4. “When sophisticated attack techniques become available to novice criminals, every organization becomes a potential target.”

    Beyond Technical Controls

    While technical security measures remain crucial, they’re no longer sufficient on their own. The human element has become the critical factor in defending against these evolved threats. This is where KnowBe4’s Security Awareness Training makes a crucial difference.

    By providing continuous, adaptive training that reflects the latest threat tactics, KnowBe4 helps organizations build a human firewall that can recognize and resist even the most sophisticated phishing attempts. With over 70,000 organizations worldwide trusting KnowBe4, the impact of this approach is clear: educated employees become an active defense layer rather than a vulnerability.

    Building Organizational Resilience

    The key to combating modern phishing threats lies in creating a security-aware culture where:

    • Employees understand the latest phishing techniques
    • Teams recognize the limitations of technical controls like MFA
    • Security awareness becomes an ongoing practice, not a one-time training

    🔒 Ready to strengthen your organization’s human firewall against sophisticated phishing attacks? Book a demo with KnowBe4 today and discover how security awareness training can transform your employees from potential vulnerabilities into active defenders of your organization’s security.


    Book Your KnowBe4 Demo Now

  • Voice Phishing Surge: New Social Engineering Attacks Leave 50% of Companies Vulnerable

    Voice Phishing Surge: New Social Engineering Attacks Leave 50% of Companies Vulnerable

    🚨 Phishing Attacks Dominate Cyber Threats in 2025: Here’s What You Need to Know

    The cybersecurity landscape has shifted dramatically in early 2025, with phishing attacks emerging as the preferred weapon in cybercriminals’ arsenal. According to recent findings, phishing has skyrocketed from less than 10% to an alarming 50% of all cyber incidents, marking a significant transformation in how threat actors operate.

    The Evolution of Phishing Tactics

    Perhaps most concerning is the rise of voice phishing (vishing), which now accounts for over 60% of all phishing engagements. Attackers have refined their approach, often starting with seemingly innocuous spam before escalating to voice calls through platforms like Microsoft Teams, ultimately convincing victims to grant remote access to their systems.

    Manufacturing and construction industries have found themselves particularly in the crosshairs, with ransomware attacks surging by 20% in Q1 2025. The notorious BlackBasta and Cactus variants alone are responsible for 60% of these incidents, demonstrating how threat actors are concentrating their efforts on proven attack methods.

    The Human Element: Your Strongest Defense or Greatest Vulnerability?

    While technical security measures remain crucial, the data clearly shows that insufficient user education continues to be the Achilles’ heel in many organizations’ security posture. This is where KnowBe4’s Security Awareness Training platform becomes invaluable, offering a comprehensive solution to strengthen what’s often the weakest link in security: human behavior.

    Why KnowBe4 Makes a Difference

    KnowBe4’s platform addresses these emerging threats head-on by:

    • Providing regular, updated training on the latest phishing tactics
    • Simulating real-world vishing and phishing attempts
    • Building a security-first culture across organizations
    • Offering measurable results in reducing human-risk factors

    Building Your Defense

    With more than 70,000 organizations worldwide trusting KnowBe4, the platform has proven its effectiveness in reducing human-risk factors and strengthening organizational security culture. As cyber threats continue to evolve, the importance of comprehensive security awareness training cannot be overstated.

    🔒 Ready to protect your organization against the latest phishing threats? Schedule a demo of KnowBe4’s Security Awareness Training platform today and take the first step toward building a more resilient security posture.

    Book Your KnowBe4 Demo Now

  • Alert: Cybercriminals Using Legitimate Software to Hijack Social Security Phishing Victims

    Alert: Cybercriminals Using Legitimate Software to Hijack Social Security Phishing Victims

    🚨 New Social Security Phishing Scam Exploits Legitimate Remote Access Tools

    In a concerning development for cybersecurity professionals, threat actors are now combining social engineering with legitimate remote access tools in a sophisticated phishing campaign impersonating the U.S. Social Security Administration. This emerging threat showcases how cybercriminals continue to evolve their tactics, making detection increasingly challenging for traditional security measures.

    The Anatomy of a Sophisticated Attack

    The Molatori cybercriminal gang has launched a particularly clever campaign that leverages two powerful elements:

    1. Official government impersonation
    2. Deployment of legitimate remote access software (ScreenConnect)

    What makes this attack especially dangerous is its use of trusted tools and institutional authority. Victims receive what appears to be an official notification about their Social Security statement, complete with convincing branding and urgent messaging. When users interact with the attachment, they unknowingly install ScreenConnect – a legitimate remote access tool that gives attackers comprehensive control over their systems.

    Why Traditional Defenses Aren’t Enough

    For IT security teams, this attack presents a unique challenge. Since the remote access tool being deployed is legitimate software used by many businesses, traditional security solutions may not flag it as malicious. This creates a dangerous blind spot where attackers can:

    • Execute commands
    • Transfer files
    • Install additional malware
    • Maintain persistent access
    • Operate without immediate detection

    Building a Human Firewall with KnowBe4

    This is where security awareness training becomes crucial. KnowBe4’s comprehensive platform helps organizations create a human firewall against these sophisticated social engineering attempts. Through realistic phishing simulations and engaging training content, employees learn to:

    • Identify suspicious communications, even from seemingly trustworthy sources
    • Verify unexpected requests through proper channels
    • Question urgent demands for action
    • Recognize social engineering tactics in real-time

    The Power of Prepared Employees

    With over 70,000 organizations worldwide trusting KnowBe4’s security awareness training platform, the evidence is clear: educated employees are your best defense against evolving social engineering threats. When your team knows what to look for, even sophisticated attacks like this Social Security campaign become easier to spot and stop.

    🤔 Are your employees prepared to recognize and respond to advanced phishing attempts that use legitimate tools and trusted authorities? Book a demo with our team today to see how KnowBe4 security awareness training can strengthen your organization’s human firewall.

    Book Your KnowBe4 Demo Now

  • The Human Firewall: Why 99% of Modern Phishing Attacks Are Outsmarting Your Security Tech

    The Human Firewall: Why 99% of Modern Phishing Attacks Are Outsmarting Your Security Tech

    The New Face of Phishing: How Social Engineering Has Replaced Malware

    In today’s cybersecurity landscape, phishing attacks have undergone a significant transformation. According to recent findings, attackers are increasingly abandoning malware-laden emails in favor of sophisticated social engineering tactics that exploit human psychology rather than technical vulnerabilities.

    The Evolving Threat Landscape 🔄

    The most concerning shift in the cybersecurity world is the remarkable effectiveness of modern phishing campaigns. According to Fortra, an astonishing 99% of phishing emails in 2024 now bypass traditional malware detection by utilizing response-based tactics like impersonation and credential theft. These attacks don’t contain malicious code that security tools can detect—instead, they manipulate users into taking actions that compromise security.

    This evolution means that organizations relying solely on traditional security solutions like malware scanning and email filtering are increasingly vulnerable. As social engineering becomes the weapon of choice for cybercriminals, the human element of security has never been more critical.

    The Rise of Hyper-Personalized Attacks 🎯

    What makes modern phishing particularly dangerous is the increasing level of personalization. Cybercriminals now harvest personal information from public databases, data breaches, and dark web records to craft highly convincing emails tailored to specific individuals.

    Imagine receiving an email that not only addresses you by name but references your recent purchases, includes details about your neighborhood, or even incorporates images of your home from public records. These personalized elements create powerful psychological triggers—fear, trust, and urgency—that bypass rational thinking and lead to snap decisions.

    AI: Scaling Sophisticated Attacks 🤖

    The situation is further complicated by artificial intelligence. Cybercriminals are now leveraging AI tools to automate and scale their personalized attacks with unprecedented efficiency. These advanced tools allow attackers to:

    • Generate convincing, grammatically perfect phishing emails
    • Create tailored content for specific individuals or organizations
    • Scale operations to target thousands of users with personalized messages
    • Rapidly adapt tactics based on success rates

    Building Human-Centered Defense with KnowBe4 🛡️

    In this new reality, technical solutions alone cannot protect your organization. KnowBe4’s Security Awareness Training addresses this critical gap by transforming your employees from potential vulnerabilities into a robust human firewall.

    KnowBe4’s approach includes:

    1. Simulated Phishing Tests – Safely exposing employees to realistic phishing scenarios, including the latest social engineering tactics
    2. Engaging Training Content – Interactive, relevant training modules that teach recognition of even sophisticated phishing attempts
    3. Continuous Learning – Regular updates that keep pace with evolving threats, including AI-generated content
    4. Measurable Results – Tracking employee improvement and identifying areas needing additional focus

    Organizations implementing KnowBe4’s Security Awareness Training report significant reductions in susceptibility to phishing attacks—often seeing click rates on simulated phishing tests drop from over 30% to under 5% within months.

    Security Culture as Competitive Advantage 🚀

    As cybercriminals increasingly target the human element of security, organizations that invest in building a security-aware culture gain a significant competitive advantage. By implementing KnowBe4’s Security Awareness Training, you’re not just reducing risk—you’re empowering employees to make security-conscious decisions across all aspects of their work.

    Is Your Organization Prepared?

    With social engineering now driving 99% of phishing attacks, traditional security tools can no longer provide adequate protection. Is your organization equipped to defend against these sophisticated human-targeted attacks?

    Book a demo with our team today to see how KnowBe4’s Security Awareness Training can transform your employees from your greatest vulnerability into your strongest security asset.

    Book Your KnowBe4 Demo Now

  • Exposed: Why Your Industry’s Email Security Gaps Could Be Putting You at Risk

    Exposed: Why Your Industry’s Email Security Gaps Could Be Putting You at Risk

    Email Security Report: How Threats Vary by Industry and What You Need to Know

    In the constantly evolving cybersecurity landscape, email remains the primary attack vector for threat actors targeting organizations across all industries. Recent data reveals fascinating patterns in how these threats are distributed, which brands are most frequently impersonated, and where critical email authentication gaps persist.

    Industry-Specific Email Threats: No One is Safe 🔍

    While all industries experienced a decline in overall email threat indices this year, certain sectors continue to face heightened targeting due to their specific vulnerabilities. Manufacturing, mining, and entertainment companies are particularly attractive targets for cybercriminals seeking to exploit intellectual property theft opportunities and potentially insecure IoT environments.

    The manufacturing sector, with its increasing reliance on connected devices and often outdated legacy systems, presents an especially vulnerable landscape. These systems, frequently running on older software without regular security updates, create openings for sophisticated ransomware campaigns employing double extortion tactics.

    Brand Impersonation: The Familiar Face of Phishing 🎭

    Brand impersonation remains one of the most effective social engineering techniques in a threat actor’s arsenal. Despite some reduction in attempts targeting DHL, companies like FedEx, Docusign, and Mastercard continue to see alarming surges in impersonation volumes.

    This trend reflects the growing sophistication of phishing techniques. Attackers leverage our inherent trust in familiar brands to manipulate recipients into clicking malicious links, downloading compromised attachments, or divulging sensitive information. The emotional and financial consequences of falling victim to these impersonations can be devastating for both individuals and organizations.

    DMARC Adoption: A Critical Gap in Email Security 🚨

    Perhaps most concerning is the state of email authentication protocols across organizations. Less than 36% of analyzed domains have implemented DMARC (Domain-based Message Authentication, Reporting, and Conformance) protocols. This leaves nearly two-thirds of business domains vulnerable to spoofing and sophisticated phishing attacks.

    Even among those who have adopted DMARC, many fail to utilize advanced reporting features like RUA (Receiver Aggregate Reporting), missing valuable opportunities to gain insights into potential threats and strengthen their proactive defense capabilities.

    How Hornetsecurity’s Solutions Address These Challenges

    HornetSecurity’s comprehensive email security solutions provide multi-layered protection against these evolving threats. Their Advanced Threat Protection service offers specialized defenses against sophisticated phishing attempts, including AI-powered detection of brand impersonation attacks that might otherwise slip through traditional filters.
    For organizations concerned about domain authentication, Hornetsecurity’s DMARC Manager simplifies the implementation and management of email authentication protocols. This tool not only helps protect your domain from being impersonated but also provides valuable reporting features that offer insight into potential spoofing attempts targeting your organization.

    By implementing industry-specific security frameworks through Hornetsecurity’s solutions, businesses can prioritize their cybersecurity investments more effectively. The platform’s advanced threat intelligence continuously monitors emerging attack patterns across industries, ensuring protection remains relevant against the latest tactics.

    Strengthening Your Email Security Posture

    Understanding these email security trends is just the first step. To truly protect your organization, consider these key actions:

    1. Implement robust email authentication protocols including SPF, DKIM, and DMARC
    2. Evaluate your industry-specific vulnerabilities and adjust security measures accordingly
    3. Conduct regular phishing awareness training for all employees
    4. Deploy advanced email security solutions with specialized phishing protection

    With nearly two-thirds of businesses still lacking proper DMARC implementation, there’s a significant opportunity to strengthen your security posture and gain an advantage over less-protected competitors. Not only does this protect your operations, but it also demonstrates to customers and partners that you take data security seriously.

    Ready to enhance your organization’s email security defenses against these evolving threats? Contact us today to learn more about implementing Hornetsecurity’s comprehensive email protection solutions for your business.


    Contact Us For Info

  • Phishing-as-a-Service Explosion: Why Your MFA Strategy Is Now Obsolete

    Phishing-as-a-Service Explosion: Why Your MFA Strategy Is Now Obsolete

    The Alarming Rise of Phishing-as-a-Service: What IT Leaders Need to Know

    Recent research from Barracuda reveals a disturbing trend in the cybersecurity landscape: phishing-as-a-service (PhaaS) platforms launched over 1 million attacks in just the first two months of 2025. This commercialization of cybercrime has democratized sophisticated phishing capabilities, putting organizations of all sizes at risk.

    Why PhaaS Should Be on Your Radar 🚨

    The PhaaS model has transformed phishing from a specialized criminal activity into a turnkey service accessible to virtually anyone. Three platforms currently dominate this underground economy:

    1. Tycoon 2FA: Responsible for 89% of detected PhaaS attacks, using encrypted scripts and Telegram for data exfiltration
    2. EvilProxy: Accounting for 8% of attacks, specializing in cloud platform compromises
    3. Sneaky 2FA: A newcomer targeting Microsoft 365 accounts with sophisticated MFA bypass techniques

    What makes this trend particularly concerning is the dramatic increase in both volume and sophistication. Phishing attacks increased 198% in the second half of 2023, and the release of generative AI tools has fueled a staggering 1,265% increase in phishing emails since late 2022.

    Multi-Factor Authentication Is No Longer Enough

    Perhaps most alarming is how these PhaaS platforms are specifically designed to circumvent traditional security measures. All three major platforms explicitly target multi-factor authentication:

    • They utilize adversary-in-the-middle techniques that capture authentication tokens
    • They employ browser identification to customize attacks
    • They check if targets are legitimate before launching, evading detection systems
    • Some even exploit Microsoft 365’s “autograb” functionality

    In this evolving threat landscape, traditional security approaches alone cannot provide adequate protection.

    Building a Multi-Layered Defense with Security Awareness Training

    While technical controls remain essential, KnowBe4’s Security Awareness Training offers a critical additional layer of protection against these advanced threats. Their comprehensive solution helps organizations:

    • Create a human firewall: Through interactive training modules that address the latest PhaaS tactics
    • Simulate real-world attacks: With phishing simulations that replicate EvilProxy, Tycoon 2FA, and other PhaaS platforms
    • Track improvement: Using metrics that demonstrate reduced susceptibility to attacks over time
    • Address multi-channel threats: Training that covers phishing across email, Microsoft Teams, Slack, SMS, and QR codes

    The impact is measurable—organizations implementing KnowBe4’s Security Awareness Training report up to 60% reduction in phishing susceptibility within 12 months, and 84% of US organizations confirm reduced employee vulnerability to phishing attacks.

    Protecting Your Organization in the PhaaS Era

    As PhaaS platforms continue to evolve, organizations need comprehensive defense strategies that combine technical controls with human-centered approaches:

    1. Implement phishing-resistant authentication methods
    2. Deploy email security tools that can detect sophisticated redirect links and QR code phishing
    3. Apply conditional access policies to limit MFA devices per user
    4. Update help-desk policies to prevent social engineering of MFA
    5. Invest in ongoing security awareness training with KnowBe4

    With the average cost of a phishing breach now reaching $4.88 million, can your organization afford to overlook the human element of cybersecurity? Book a demo of KnowBe4’s Security Awareness Training today to see how you can transform your employees from your greatest vulnerability into your strongest defense against the rising PhaaS threat.

    Book Your KnowBe4 Demo Now

  • KnowBe4: Unraveling the Leader in Cybersecurity Training

    KnowBe4: Unraveling the Leader in Cybersecurity Training

    KnowBe4: Unraveling the Leader in Cybersecurity Training

    KnowBe4 has emerged as a pivotal force in the realm of cybersecurity, offering a comprehensive suite of training modules designed to equip organizations with the knowledge to fend off cyber threats. Through a blend of engaging training material and automated phishing simulations, KnowBe4 arms employees with the necessary skills to identify and mitigate potential cyber attacks, fostering a culture of security awareness training across various sectors.

    At the core of KnowBe4’s success lies its commitment to innovation within the cybersecurity training landscape. By continuously updating its training modules to reflect the latest cyber threats and trends, KnowBe4 ensures that organizations are always one step ahead. This proactive approach to cybersecurity education is complemented by KnowBe4’s use of real-world phishing simulations, allowing employees to experience the dynamics of actual phishing attempts in a controlled environment.

    Unlocking the Essence of KnowBe4

    KnowBe4 Security Awareness Training

    KnowBe4 stands out in the cybersecurity space through its unique amalgamation of automated phishing simulations, comprehensive training materials, and an extensive library of training modules. This blend not only demystifies the complex world of cyber threats but also empowers organizations to build a resilient and informed workforce. KnowBe4’s platform is designed to cater to various learning styles, ensuring that every employee can effectively contribute to their organization’s cyber defense strategy.

    How KnowBe4 Empowers Organizations Through Cybersecurity Training

    KnowBe4 empowers organizations by providing a robust framework of training modules that cover a wide range of cyber threats, including real-world phishing scenarios. Its managed service approach ensures that businesses can implement a tailored security training program that aligns with their specific needs and threats. By leveraging KnowBe4’s comprehensive training tools, organizations can significantly enhance their employees’ ability to recognize and respond to cyber threats, effectively reducing the risk of a successful attack.

    The Unique Approach of KnowBe4 to Security Awareness

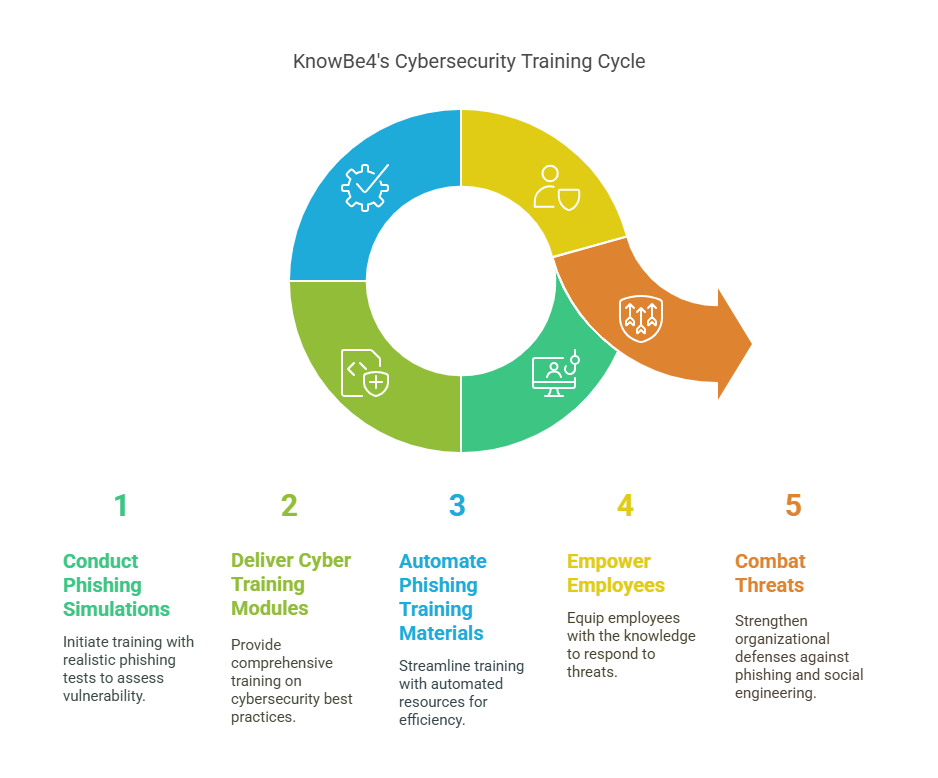
    KnowBe4s Security 
 Awareness Training Cycle

    KnowBe4’s unique approach to security training revolves around creating a culture of continuous learning and vigilance. Unlike traditional security training programs, KnowBe4 engages users with interactive content and real-life simulations that mirror the latest phishing tactics. This method ensures that employees are not only well-versed in theoretical knowledge but are also prepared to apply this knowledge in practical, real-world situations, making it a leader in fostering security awareness.

    Analyzing KnowBe4’s Offerings

    KnowBe4’s offerings are a testament to its leadership in the cybersecurity training industry. Its platform provides a comprehensive suite of tools and resources that cater to the evolving needs of modern organizations seeking to bolster their cyber defenses.

    Human Risk Management

    Human risk is growing exponentially as technology becomes more woven into everyday routines. Recent research from KnowBe4 indicates 62% of surveyed organizations experienced one or more cyber incidents in the past year linked to human risk.  Their new HRM+ platform focuses on combatting this specific area.  On average, these businesses encountered three different types of breaches three times each, with 96% involving employees who clicked malicious links or opened harmful attachments.

    The Pros of Implementing KnowBe4 in Your Security Strategy

    Integrating KnowBe4 into an organization’s security strategy introduces a proactive layer of defense against cyber threats.

    KnowBe4’s training solutions offer several advantages, including increased awareness of phishing scams, a reduction in successful cyber attacks, and the cultivation of a security-first culture within organizations. By leveraging KnowBe4’s automated phishing simulations and engaging training modules, companies can significantly enhance their workforce’s ability to identify and neutralize potential threats, thereby strengthening their overall security posture.

    The Verdict from the Market

    KnowBe4’s market standing is a reflection of its effectiveness in enhancing organizational security through comprehensive training programs.

    How Businesses Are Leveraging KnowBe4 for Enhanced Security

    Organizations across industries are leveraging KnowBe4’s training solutions to fortify their defenses against cyber threats. The platform’s user-friendly approach and up-to-date content have made it a preferred choice for businesses seeking to elevate their security awareness levels.

    Customer Insights: Real Feedback from KnowBe4 Users

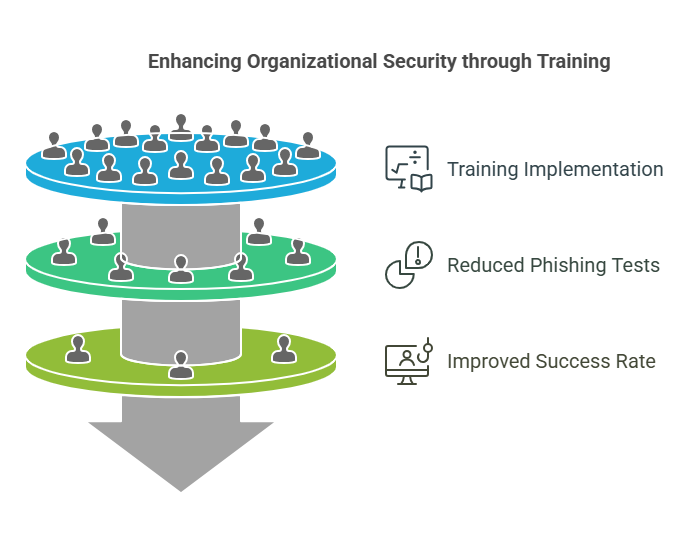
    Enhancing Organizational Security Through Training

    Feedback from KnowBe4 users highlights the platform’s impact in reducing the frequency and success rate of phishing tests, underscoring the tangible benefits of its training programs in improving organizational security.

    Why KnowBe4 Stands Out Amidst a Sea of Options

    KnowBe4 sets itself apart in the crowded field of cybersecurity training by understanding that the human element is both the biggest asset and the weakest link in cyber defense. Its platform combines security awareness with interactive training, making it easier for organizations to foster a culture of vigilance against phishing attempts and other cyber threats. KnowBe4’s platform continually updates its fresh content, ensuring users are prepared for the latest security challenges. This approach not only educates but empowers employees across organizations worldwide to make smarter security decisions, solidifying KnowBe4’s position as a leader in the awareness training platform space.

    Book Your KnowBe4 Demo Now